 In 2016, an unnamed US energy company left some 30,000 records (containing information about its security assets) exposed for more than two months (a total of 70 days), in violation of energy sector cyber security regulations. When the incident was initially reported, the name of the company was withheld.
That company has now agreed to a $2.7 million-dollar settlement, and its name has now been made public, along with some additional details about the incident.
Initially, the company admitted that they unintentionally exposed the database in question, but that it contained fake data. As the investigation into the matter continued, it became apparent that the data was not only real, but that it included hashed passwords for administrators that hackers could have easily reverse-engineered. PG&E subsequently reversed their fake data assertion.
The exposed data was found by independent security researcher Chris Vickery, who indicated at the time that the database contained details for some 47,000 computers, virtual machines, servers and other devices.
In addition to that a number of non-encrypted email passwords were found, along with 120 encrypted passwords. In Vickery’s words, “This would be a treasure trove for any hostile nation-state hacking group.”
According to the official NERC notice regarding the incident:
“The data was exposed publicly on the internet for 70 days. The usernames of the database were also exposed, which included cryptographic information of those usernames and passwords. Exposure of the username and cryptographic information could aid malicious attackers in using this information to decode passwords.”
Once PG&E was made aware of the problem, it took a server offline, which removed the exposed data. They also brought in third-party forensic experts to investigate, and as a result of that investigation, revised a number of their security policies.
Overall, the company’s handling of the matter was spotty at best, but in light of the record-setting fine, the hope is that we won’t see a similar instance of carelessness in the future.
 It’s official, Apple now has company in the Trillion Dollar Club as Amazon’s stock surged past $2,000, briefly pushing the company’s total value to just over the trillion-dollar mark.
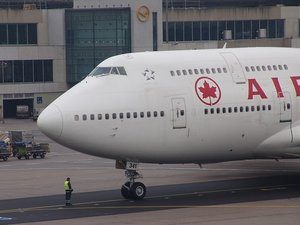 If you fly Air Canada and use their mobile app, it may be time to change your password. The company recently announced that between August 22nd and August 24th of this year, they detected “unusual log-in behavior,” and that a small fraction (some 20,000) of their 1.7 mobile app users may have had their data compromised as a result.
 Tech Support scams are nothing new, but they are getting increasingly sophisticated. Worse, tech giants like Google are finding it notoriously difficult to detect them.
 Business Email Compromise (BEC) attacks are a major threat, costing business nearly three billion dollars a year.
 2017 was “The Year of Ransomware.” It saw an incredible number of ransomware attacks and infections, paired with a tremendous number of innovations.
 Do you own an iPhone 8? If so, you may have problems. Apple has recently reported that a small percentage of iPhone 8s “contain logic boards with a manufacturing defect.
 A new study recently published by Sitchfast Technologies paints a grim picture of the threat landscape for small and medium-sized business. Their key finding? A staggering 60 percent of small businesses that suffer a data breach of any magnitude go out of business within six months. Worse, one business owner in three does not have a plan or safeguards in place to prevent a breach.
 Researchers operating out of the University of Florida, Stony Brook University and Samsung Research America have made a disturbing discovery. Millions of Android smartphones manufactured by eleven different OEMs (Original Equipment Manufacturers) were found to be vulnerable to attack via AT Commands.
 The great state of Texas has 15.2 million registered voters. Unfortunately, personal details belonging to nearly all of them (14.8 million) have been compromised, but don’t blame the state’s election officials.