
 There’s a new report out, authored by ProofPoint, and its findings for business are grim.
It’s no secret that businesses of all shapes and sizes are coming under increasing fire from hackers around the world.
Now we have hard data that shows us exactly how big of an increase we’re seeing.
Here are some of the key findings in the report:
Email fraud attacks targeting businesses have increased 25 percent in the last quarter alone
They have increased by a staggering 85 percent from this time last year
Phishing links sent via social media platforms have increased by 30 percent
60 percent of those phishing links specifically targeted individual contributors and lower-level corporate management
23 percent of attacks targeted employees working in operations and production
Incidents of customer support fraud increased by 39 percent, compared to the previous quarter. This increased a whopping 400 percent compared with this time last year
Nick Frost (a co-founder of the Cyber Risk Management Group) had this to say about the disturbing report:
“Key to this is engineering emails and spoofing email addresses to a level of sophistication that fails to alert the recipient that there is anything suspicious about the email. Techniques such as web crawling and web scraping are able to collect and collate key information about an individual that can be used in crafting an email, accompanied by a link (as part of a phishing attack) to an unsuspecting user.
Whilst there are many legitimate web crawlers and many are enabled for business reasons, there may be organizations and individuals that wish for their information not to be collected and shared either for legitimate or adversarial purposes. There are tools that organizations can adopt that prevent or even delay web crawlers.”
Training is the first line of defense here. If you’re not doing it already, you should be holding regular phishing simulations so your employees become adept at spotting them.
 Perhaps the most significant change to the browser is the addition of a new password manager, which will offer to generate a random password when you sign into a website for the first time. The randomly generated password will be securely tucked away inside your Google Account and synced across both desktop and mobile versions of Chrome.
 The Internet on devices continues to be a major problem when it comes to security. Unfortunately, a big part of the reason why comes down to end users. Recently, Bitdefender released a new report entitled “The IoT Threat Landscape And Top Smart Home Vulnerabilities in 2018,” and it paints a grim picture indeed.
 Microsoft is making some long overdue and welcome changes to Outlook to include the Windows and the Web-based version.
 Microsoft has been making two major Windows 10 releases every year, giving businesses 18 months before they need to move to the next update. This plan and schedule is part of the company’s “Windows as a service” paradigm, designed to ensure that Windows 10 gets new features, as opposed to the company’s former practice of a new Windows release every three years.
 Do you use the Chrome browser extension for the MEGA file storage service? If you do, please read this article carefully. The official extension for that service has been compromised. It has been replaced with a malware version that has the capability to steal user login data for a number of popular websites, including Github, Google, Amazon, Microsoft and more.
 In 2016, an unnamed US energy company left some 30,000 records (containing information about its security assets) exposed for more than two months (a total of 70 days), in violation of energy sector cyber security regulations. When the incident was initially reported, the name of the company was withheld.
 It’s official, Apple now has company in the Trillion Dollar Club as Amazon’s stock surged past $2,000, briefly pushing the company’s total value to just over the trillion-dollar mark.
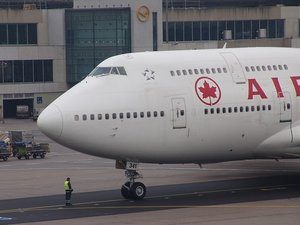 If you fly Air Canada and use their mobile app, it may be time to change your password. The company recently announced that between August 22nd and August 24th of this year, they detected “unusual log-in behavior,” and that a small fraction (some 20,000) of their 1.7 mobile app users may have had their data compromised as a result.
 Tech Support scams are nothing new, but they are getting increasingly sophisticated. Worse, tech giants like Google are finding it notoriously difficult to detect them.


