 There’s a new threat to point of sale (POS) systems coming out of Russia, according to security researchers from Booz Allen Hamilton. The malware, which they’re calling “RtPOS” isn’t bleeding edge technology, and does not approach the level of sophistication of other recently discovered strains, but that doesn’t mean it should be taken lightly. These strains include RawPOS, MajikPOS, UDPOS, and Treasure hunter.
In its current incarnation, it has a limited feature set and is basically a RAM scrapper. Once deployed, it will watch a PC’s RAM looking for text patterns, which are saved to a local DAT file. Of interest, it doesn’t currently appear to have any sort of networking capability, so when the data is collected and stored, it has no means of actually porting it to a command and control server (yet).
There are two competing theories as to why this software is the way it is. One theory is that it’s simply a rough draft. A work in progress. Although relatively benign in its current incarnation, it would be quite easy for the authors to add enhancements to the code, and possibly to update the software remotely, turning this “nonthreatening” software into a true menace in the blink of an eye.
Another theory is that RtPOS is one part of a multi-part, much more subtle attack. The purpose of the software is simply to infect and collect data, leaving it to a separate process to exfiltrate the data at irregular intervals, which would be more difficult to detect, and unlikely to draw attention.
At present, there’s no clear indication which theory is correct, but both ideas are disturbing. As ever, vigilance is the key. Hardly a day goes by that researchers somewhere in the world don’t discover some new threat. This is but the latest.
 Quick question – how much do the world’s cyber criminals make every sixty seconds?
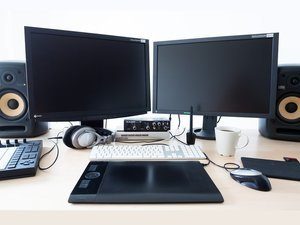 It may sound like something straight out of a science fiction movie, but recently, researchers have made a disturbing discovery. Using nothing more than an off-the-shelf microphone, it’s possible for an attacker to determine what content you’re viewing on your computer monitor.
 Telecommunications giant T-Mobile is the latest victim of a large-scale data breach, with personal data belonging to more than two million of its customers having been leaked. The exposed information included customer name, phone number, email address, billing zip code, account number and whether the account was pre-paid or post-paid.
 Android users have a new threat to contend with, according to a sixteen-page whitepaper outlining a new malware strain.
 According to a recent survey conducted by Pew Research Center, 54 percent of teens say that they spend too much time on their cellphones.
 Earlier this year, Microsoft announced that it had entered into a partnership with Open Whisper Systems, the makers of the Signal app. The purpose of the partnership was to bring Signal’s open source, end-to-end encryption protocol to Skype.
 Google has introduced a new Gmail feature called “Confidential Mode,” which seeks to make sending and receiving important or sensitive emails more secure. Unfortunately, it may have inadvertently created as many problems as it solves.
 Do you use Photoshop? Does anyone who works for you use it? If so, you’ll want to apply the latest security patch immediately.
 Intel has had a tough time of things so far this year. The most recent trouble stems from yet another newly discovered security flaw in the company’s processors, bearing the inelegant name of “L1 Terminal Fault,” or “Foreshadow” by those who have discovered it.