
 If you’re like most people, you probably rely heavily on the GPS function of your phone. Type in an address and your phone helpfully guides you, turn by turn, to your destination. It’s one of the most often utilized features of a smartphone, and of course, the hackers are very interested in interfering with it.
Until now though, hackers have been unable to fool humans into driving to the wrong destination by hacking their GPS, because their instructions often make no sense given the prevailing terrain features the humans are seeing on the road. For instance, nobody is going to turn left into a Jiffy Lube parking lot or a corn field just because GPS says to (unless your destination was Jiffy Lube, of course).
That’s changing, thanks to researchers from Virginia Tech and the University of Electronic Science and Technology of China.
The team has devised a way to hack into a GPS system and spoof the results well enough to fool humans, giving bogus driving directions that seem to make sense given local conditions, and as such, don’t raise red flags.
Accomplishing the task was no small feat, involving the creation of an algorithm that works in something close to real time. This along with a portable device for spoofing GPS that can be attached to the car of your target or placed in a trailing car. Its effective range is about fifty meters.
Once the equipment is in place, the algorithm crafts GPS inputs that follow the real world road network, allaying suspicion in 95 percent of the team’s test cases, while still ultimately sending the target to the wrong destination.
There are any number of ways this exotic type of attack could be used, but the two primary use cases would be to intentionally steer the target into hazardous road conditions, or to lure them to an isolated area where a physical attack could be carried out.
Unfortunately, in the months and years ahead, we can probably count on seeing both.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Positive Technologies has just released a new report that paints a grim picture for IT professionals. If your sense is that the number of cyberattacks are increasing, you’re not wrong. In fact, it’s probably worse than you realize.
 A majority of business owners from around the world (68 percent) feel that they’re better prepared to ward off a cyberattack and prevent a data breach than their competitors. This is a figure which is up 8 percent over last year’s statistic for the same question. This, according to a recent survey by FICO.
 According to the Kremlin, Russia prevented almost twenty five million cyber-attacks during the World Cup this year.
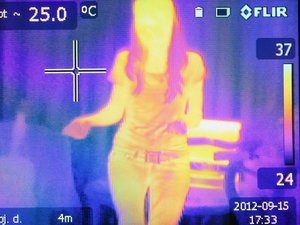 As if there weren’t enough ways for hackers to steal your passwords, now, there’s thermal imaging. If that sounds like something straight out of a science fiction movie, think again.
 Do you use Timehop? If you’re not sure what that is, it’s a popular, clever little app that reminds social media users about posts they’ve made in the past. It can be quite handy, especially if you’re active on numerous social media accounts.
 Researchers from the digital security firm ESET have recently spotted a new malware campaign with a nasty twist. It was created using a legitimate security certificate stolen from D-Link.
 Apple recently released an updated version of iOS, 11.4.1. They did so quietly, and without much fanfare, but the update includes one very powerful and exciting security update that’s deserving of special attention.
 There’s a lot to like about the contents of Adobe’s most recent “Patch Tuesday” update. It’s well worth downloading and installing, even if you normally take a pass on all but the most critical updates.
 It’s no secret that there are legions of scammers and spammers haunting the virtual halls of Facebook. As the world’s largest and most influential social networking site, it’s a natural target, making its masses of users natural targets, too.


