


One compliance effort can support more than one framework, but it shouldn’t treat them as interchangeable. IT compliance consulting in Raleigh can map overlapping controls together while keeping each framework’s distinct evidence and documentation needs clear. For example, NIST 800-171 is used to assess cybersecurity controls, according to the National Institute of Standards and Technology.
It’s reasonable to want one coordinated plan instead of separate, confusing checklists. This article explains how multi-framework compliance work can be organized, what affects the path to audit readiness, and how to think about timing without relying on a one-size-fits-all promise. You’ll also see what to expect from compliance support for businesses in North Raleigh and across the Triangle, from assessing current practices to identifying practical next steps.
Key Takeaways
- Audit readiness timelines depend on your current security controls, documentation gaps, and the work needed to address them.
- A coordinated assessment can identify which compliance requirements share controls and where separate evidence is still needed.
- Clear records of policies, safeguards, and remediation help make compliance work easier to demonstrate during an audit.
- Local businesses can use consulting support to turn assessment findings into practical next steps for their environment.
How quickly can your compliance services make my business audit-ready?
For Raleigh businesses, audit readiness depends on existing controls, documentation gaps, and the work needed to address them. Start by assessing those factors against the requirements that apply to your business.
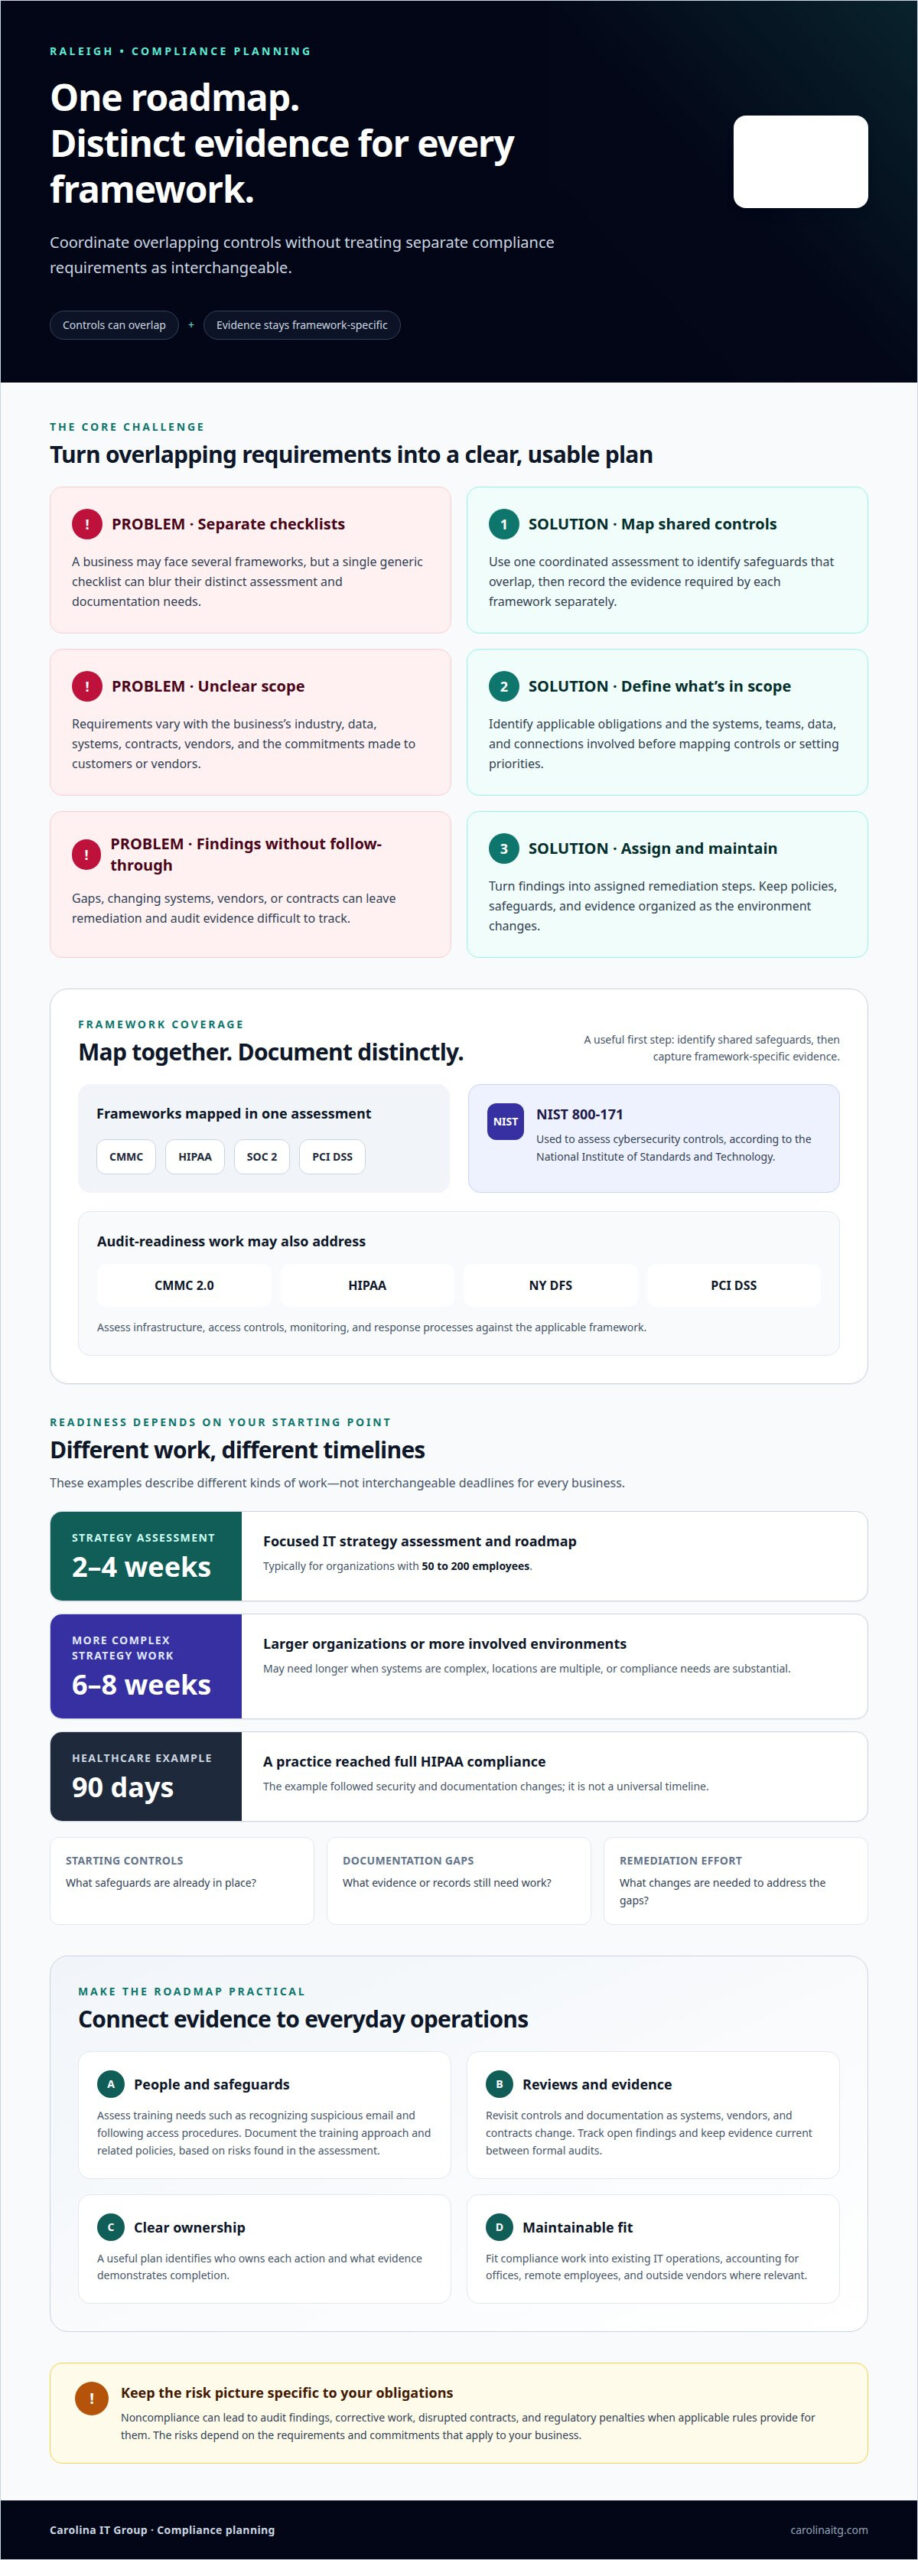
A focused IT strategy assessment and roadmap typically takes 2 to 4 weeks for organizations with 50 to 200 employees. Larger organizations with complex systems, multiple locations, or substantial compliance needs may need 6 to 8 weeks for strategy work. A healthcare-practice example reached full HIPAA compliance in 90 days after security and documentation changes. These are different kinds of work, so they aren’t interchangeable deadlines for every business.
To compare Raleigh consulting firms, examine service scope, relevant certifications, and reviews together. Look for a clear assessment process, documented findings, and a roadmap tied to your framework and contract obligations.
Noncompliance can lead to audit findings, corrective work, disrupted contracts, and regulatory penalties when applicable rules provide for them. The risks depend on the requirements that apply to your business and the commitments you have made to customers or vendors.
Awareness Training and Compliance Support
Cybersecurity consulting can connect technical safeguards with employee practices. A practical assessment identifies training needs, such as recognizing suspicious email or following access procedures. Compliance support can help document the training approach and related policies, so employees understand how daily actions contribute to security evidence. Make sure the plan addresses risks identified in the assessment rather than relying on generic awareness materials.
Ongoing Audits and Managed Compliance
Ongoing reviews revisit controls and documentation as systems, vendors, and contracts change. A managed process can organize recurring reviews, track open findings, and keep evidence current between formal audits. Some consultants also provide virtual CISO services to guide cybersecurity strategy and risk assessment without serving as an in-house executive. Before choosing a model, compare its review schedule, reporting, and decision-making responsibilities. Continuous review can help identify gaps before an audit deadline.
Can your data compliance services cover multiple frameworks at once?
Yes. A coordinated roadmap can align overlapping controls while preserving each framework’s distinct evidence and assessment needs.
Framework Coverage
CMMC, HIPAA, SOC 2, and PCI DSS can be mapped in one assessment. The National Institute of Standards and Technology describes NIST 800-171 as a framework used to assess cybersecurity controls. A useful first step is to identify shared safeguards, then record framework-specific evidence separately. Organizations should also consider which data, systems, contracts, and vendors fall within scope. That keeps a partner’s roadmap tied to actual business obligations, not a generic checklist.
Audit Readiness
For CMMC 2.0, HIPAA, NY DFS, and PCI DSS audit readiness, the work depends on applicable obligations and existing evidence. An assessment can map infrastructure, access controls, monitoring, and response processes to the relevant framework. A managed service may support continuous tracking, but it doesn’t make distinct frameworks interchangeable. Ask how findings become assigned remediation steps, how evidence stays organized, and how the roadmap reflects changes to systems or contracts.
Federal and North Carolina requirements for a Raleigh business depend on its industry, the data it handles, and its contracts. Begin a compliance review by identifying those factors, then map applicable obligations to the frameworks and controls being assessed.
For healthcare organizations, HIPAA-related support can connect security reviews with documentation and patching practices. An assessment can identify systems that need updates, record remediation, and show how safeguards relate to sensitive health information. This gives teams a clearer basis for audit preparation.
For a practical framework-mapping conversation, discuss your compliance needs.
Compliance consulting in North Raleigh and the Triangle
IT compliance consulting in Raleigh can include requirements mapping, control assessments, evidence organization, and remediation planning. Related work may address network security, cloud environments, and operational processes. The right scope depends on your data, contracts, systems, and the frameworks relevant to your business.
What IT compliance consulting services are available in Raleigh, NC? Businesses can seek help assessing controls, organizing audit evidence, reviewing security practices, and building a compliance roadmap. IT consulting can also connect findings to changes in infrastructure, access, and ongoing operations.
For North Raleigh and Triangle organizations, start by defining which systems and teams fall within scope. A business with several offices, remote employees, or outside vendors may need the assessment to account for each connection and responsibility. The consulting process can then prioritize gaps by operational impact and outline how to deploy corrective changes without overlooking business needs.
When choosing a service provider, look for an approach that fits your environment and a clear explanation of the work. A useful plan identifies who owns each action, what evidence demonstrates completion, and how network or vendor changes affect the review. Make sure the consulting work fits existing IT operations rather than creating a separate process that staff can’t maintain.
For a practical discussion of your environment and next steps, connect with the team.
Carolina IT Group: IT Consulting
Carolina IT Group provides IT Consulting and Compliance Services for businesses working toward audit readiness in Raleigh, Greenville, and Wilmington. Turn to the team when framework requirements are difficult to translate into clear security actions or assessment findings need a practical response.
IT Consulting can connect compliance priorities with your existing technology environment. Compliance Services support preparation for regulatory reviews, while Managed IT Services and Cybersecurity help support the systems and safeguards involved. Discuss your business needs and the frameworks relevant to your operations to focus the work on useful priorities rather than generic checklists.
Contact Carolina IT Group to discuss your compliance and IT consulting needs.
Turn compliance priorities into your next steps
You don’t need to tackle every compliance gap at once. Start by deciding which risk matters most to operations, who owns the response, and what evidence will show progress. A focused plan helps leadership assign work while keeping day-to-day responsibilities in view.
With IT compliance consulting in Raleigh, your next step is to turn audit priorities into a practical plan for your business. Carolina IT Group offers Managed IT Services, Cybersecurity, and Backup and Disaster Recovery to support the technology and protection needs connected to that work.
Bring your priorities and questions to a conversation with the team. Contact Carolina IT Group to discuss a clear path forward. Steady, well-defined steps can help your business move ahead with greater confidence.
Frequently Asked Questions
Which Raleigh IT compliance consultants specialize in HIPAA, PCI DSS, SOC 2, or CMMC?
Consultant fit depends on the framework and industry, not a general “compliance” label. Carolina IT Group’s stated industry-specific work includes HIPAA-compliant security for healthcare and SOX compliance assistance for finance. For PCI DSS, SOC 2, or CMMC, look for demonstrated experience with that specific framework, relevant deliverables, and a scope that matches your contracts.
What should Raleigh businesses look for when choosing an IT compliance consultant?
Choose a consultant who can explain how the work connects to your business operations. Ask what the assessment covers, how findings are prioritized, and how remediation responsibilities are recorded. If a vendor’s access affects systems in scope, for example, the plan should explain how that dependency is handled. Clear reporting helps leaders understand which decisions and resources are needed.
What are the main steps in an IT compliance assessment and remediation project?
A typical project defines scope, reviews relevant controls and evidence, records gaps, prioritizes remediation, and documents completed work. If an assessment identifies an outdated system, for example, the remediation plan can name an owner, describe the corrective action, and capture evidence of completion. This creates a traceable record for internal review and helps teams track unresolved items.
How long does IT compliance consulting typically take for small and midsize businesses?
A focused IT strategy assessment and roadmap typically takes 2 to 4 weeks for organizations with 50 to 200 employees. That timeframe describes assessment and planning, not necessarily the time needed to complete every corrective action. More complex environments, multiple locations, or substantial compliance needs may extend strategy work to 6 to 8 weeks.
How do Raleigh IT compliance consulting firms compare by services, certifications, and reviews?
Compare service scope, relevant certifications, and reviews together. Look for a clear assessment process, documented findings, and a roadmap tied to your framework and contract obligations.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.


Leave a Reply
You must be logged in to post a comment.