
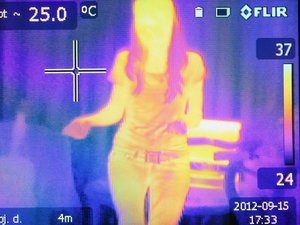
 As if there weren’t enough ways for hackers to steal your passwords, now, there’s thermal imaging. If that sounds like something straight out of a science fiction movie, think again.
Researchers from the University of California at Irvine recently discovered and demonstrated a technique that involves the use of a thermal imaging camera to capture heat traces left by human fingertips as they type passwords into a keyboard. In fact, their technique is effective for up to thirty seconds after the user removes his hands from the keyboard.
Per the researchers, “Although thermal residue dissipates over time, there is always a certain time window during which thermal energy readings can be harvested from input devices to recover recently entered, and potentially sensitive information.”
The team tested their technique using off the shelf technologies, and on four different keyboards. Their findings indicated that a full password could be obtained by scanning for thermal residues on those keyboards, provided that the scan was taken within thirty seconds of the first key being pressed. After a full minute, it was still possible to obtain partial passwords.
They used an FLIR camera on a tripod set two feet from the keyboards being tested, and the results of their findings were published in a paper called simply, “Thermanator.”
FLIR makes a number of different camera models that can capture heat. Their most basic model, the FLIR One Pro is a $400 accessory available as a smartphone attachment. Some phones (like the CAT S61) ship with the FLIR module embedded in the technology.
The team noted that the ease with which a password could be detected in this manner had a lot to do with the typing style of the target being monitored. Passwords entered by “hunt and peck” typists could be gleaned between 19.5 and 31 seconds, while passwords entered by touch typists took upwards of 50 seconds to be gleaned.
Obviously, this is a fairly exotic form of attack. Although it utilizes off the shelf technology, it would require an extraordinary level of access to set the equipment up, and an extraordinary lack of vigilance on the part of security personnel not to detect the equipment in relatively short order. Even so, it’s certainly within the realm of possibility, and one more thing to be on guard against.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Do you use Cortana? It’s a handy virtual assistant (like Siri) built into Windows 10. Unfortunately, as useful as she is, there’s a problem. Even if you don’t use Cortana yourself, take heed: Microsoft has recently issued a security update based on findings by McAfee researchers.
 What’s old is new again.
 How many web apps do you have on your phone? Probably a ton. Here’s something you likely didn’t know. Based on the latest research from Positive Technologies, nearly half of them (48 percent) are vulnerable to unauthorized access.
 Another week, another new threat. This time, in the form of a new strain of malware that researchers are calling InvisiMole. The new threat was discovered by researchers at ESET, who found it on a number of hacked computers in Russia and the Ukraine.
 Last year’s Wannacry attack was bad, but in many ways, it was a self-inflicted wound. According Webroot’s recently published “Annual Threat Report,” almost all of the machines that succumbed to the Wannacry attack were running Windows 7. That attack is estimated to have caused in excess of $4 billion in total losses.
 If you use Amazon’s Cloud MP3 Locker to store your music online, now is the time to start looking for a new home for it. Last year, the company announced that they were ending the service, but didn’t provide a firm date. April 30, 2018 will be the last day you’ll be able to access your music if you don’t take action.
 There are some big changes coming to Facebook, which may have some serious unintended consequences.
 Another week, another high-profile data breach. This time, it’s Under Armour in the hot seat. Under Armour acquired the MyFitnessPal app back in February 2015, and the company recently announced that their new acquisition was hacked in late February 2018.
 There’s a new type of hacking attack to be concerned with, and it’s growing by leaps and bounds. Called “Crypto-Jacking,” it’s a process by which malicious code is placed on websites. When the sites are visited, the code secretly siphons off a portion of the affected user’s PC, laptop, or smartphone’s processing power and uses it to mine for various cryptocurrencies so that the hackers can profit from it.


