
 On May 14th, the Billings Clinic in Montana issued a breach notification statement, which explained that they detected unusual activity within one of its employee’s email accounts.
The employee in question was traveling overseas on a medical mission when the email account was compromised.
“As a result of the forensics investigation, we learned that an unauthorized individual had access to emails and attachments within that one account, some of which included patient information.”
As for scope and scale, information on more than 8,400 individuals was exposed. While the data varied from one patient to the next, the data included patient names, dates of birth, contact information, medical record numbers, internal financial control numbers, diagnoses, and some information about medical services received.
The incident highlights a common, but often overlooked problem.
As analyst Rebecca Herold explains:
“It is very common for data and devices to be hacked while traveling and for those who were hacked to not even realize it. People are often unaware of what is going on around them when they are travelling. They are using any charger station they can find, they speak loudly, and they use free Wi-Fi.
Shoulder surfing is also still very common; it’s a decades-old tactic that still works effectively today. The skimmers on charging stations are increasing in use. Don’t think that if you are in a frequent flyer lounge that these things do not happen there; they happen in those exclusive lounge areas possibly more than in other places.”
The bottom line is, any time your employees are away from your office, the risks of hacking increase. While there are no simple solutions, it bears making your employees aware of the added risks any time they’re travelling. It’s far from a perfect solution, but it’s a good place to start.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
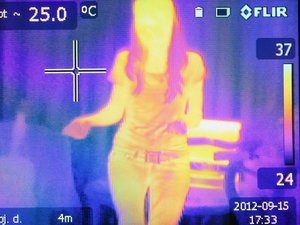 As if there weren’t enough ways for hackers to steal your passwords, now, there’s thermal imaging. If that sounds like something straight out of a science fiction movie, think again.
 Do you use Timehop? If you’re not sure what that is, it’s a popular, clever little app that reminds social media users about posts they’ve made in the past. It can be quite handy, especially if you’re active on numerous social media accounts.
 Researchers from the digital security firm ESET have recently spotted a new malware campaign with a nasty twist. It was created using a legitimate security certificate stolen from D-Link.
 There’s a lot to like about the contents of Adobe’s most recent “Patch Tuesday” update. It’s well worth downloading and installing, even if you normally take a pass on all but the most critical updates.
 Internet security researcher Vinny Trola recently made a huge and disturbing discovery. A marketing firm called Exactis had left a massive database unsecured, allowing anyone who stumbled across it to access it.
 While a significant percentage of Americans are suspicious of government spending beyond the essentials, there’s at least one notable exception, according to a recent survey conducted by SecurityFirst.
 Another week, another high-profile data breach. This time, Adidas and their online store was the target.
 Menlo Security has recently published a new report that will probably dismay you if you’re a business owner.
 Do you use Cortana? It’s a handy virtual assistant (like Siri) built into Windows 10. Unfortunately, as useful as she is, there’s a problem. Even if you don’t use Cortana yourself, take heed: Microsoft has recently issued a security update based on findings by McAfee researchers.


