 Menlo Security just released their third annual “State of the Web” report and it’s not pretty. The headline finding is that 42% of the top 100,000 sites as ranked by Alexa are more dangerous than you think.
The report defines a risky site as one that meets one of three criteria:
The site, or one of its associated background sites (from which news articles or video is pulled), is running software with a known security vulnerability
The site has been used to launch attacks or distribute malware
The site has suffered a security breach in the past twelve months
This first point is key, and often overlooked by security professionals. Any time your website is pulling content from another source, it creates an opening that a hacker could potentially exploit. Worse, most security professionals lack the tools to properly monitor those connections.
As bad as that sounds, there’s an even worse detail lurking in the pages of the report, and that concerns emails.
Hackers are increasingly moving away from setting up their own domains. Instead, they’re preferring to create a subdomain of a compromised, legitimate domain, which makes it harder to spot. Amir Ben-Efraim, the CEO of Menlo Security, had this to say about the issue:
“It is far easier to set up a subdomain on a legitimate hosting service than use other alternatives – such as trying to hack a popular, well-defended site or to set up a brand-new domain and use it until it is blocked by web security firms. Legitimate domains are often whitelisted by companies and other organizations out of a false sense of security, giving cover to phishing sites.
Also, hosting services typically allow customers to set up multiple subdomains. For example, researchers found 15 phishing sites hosted on the world’s 10 most popular domains.”
The bottom line is: The web and even the most popular sites on it, aren’t nearly as safe as you think.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Sophos has released the results of their annual “State of Endpoint Security Today”, and it doesn’t paint a pretty picture. A full 54% of companies surveyed reported having been hit by a ransomware attack in 2017. Another 31% reported that they expect to be on the receiving end of such an attack in the near future.
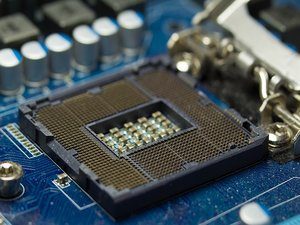 Security researchers from around the web are reporting finding an increasing number of instances of proof of concept (PoC) code that incorporates the recently discovered Spectre and Meltdown vulnerabilities.
 Oracle is currently the third-largest provider of POS (Point of Sale) software on the market today, which means that there’s a fairly good chance you’re using an Oracle POS system. If you are, there’s trouble ahead. A recently discovered security flaw could put your system at risk.
 Google recently released their Play Store stats for 2017. The results are both encouraging and disheartening. Overall, Google caught and removed more than 700,000 malicious apps from the Play Store, minimizing their impact on the company’s massive Android user base.
 Recently a critical flaw was found inside every Intel chip made during the last decade. The flaw makes two different exploits possible. These exploits have been dubbed “Meltdown” and “Spectre.”
 All companies collect data on their customers, but some are better than others when it comes to being upfront about what kinds of data are collected. Over the past year, Microsoft has made many moves that have been well-received by their enormous user base. They’ve become increasingly transparent and offer an unprecedented level of control to the users themselves.
 Do you play Blizzard online computer games such as World of Warcraft, Diablo III, Hearthstone, Starcraft II, or Overwatch? If so, there’s a potential problem you need to be aware of.
 By now, we’ve seen enough large-scale Point of Sale (POS) credit card thefts that patterns are beginning to emerge. Some companies follow the general arc of the narrative better than others and deserve credit for doing so, but in the end, the story is about the same.
 It’s official, the first macOS malware of 2018 is here. Discovered by an independent security researcher and dubbed “OSX/MaMi,” the code is functionally similar to DNSChanger malware.