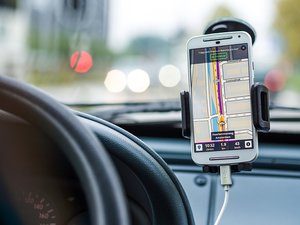
 A duo of researchers stumbled across a series of vulnerabilities in literally hundreds of GPS services that leave sensitive GPS tracking data open to hackers. Dubbed “Trackmageddon” by the researchers, the vulnerabilities span a range of weaknesses that include default or easy-to-guess passwords, IDOR (Insecure Direct Object Reference) issues, insecure API endpoints, and data collection folders that are entirely unsecured.
The reason so many different tracking services are impacted is that most of them rely on the same online software to deliver their services, and that software (believed to be designed by ThinkRace, one of the largest vendors of GPS tracking devices) itself is flawed. As more and more companies license it, the issues spread, exposing the data of an increasing number of customers who are entirely in the dark about how vulnerable their location data is.
The researchers have made attempts to contact the vendors offering GPS tracking services with vulnerabilities, but so far, have met with only limited success. According to their report:
“We tried to give the vendors enough time to fix (also respond for that matter) while we weighed this against the current immediate risk of the users.
We understand that only a vendor fix can remove a user’s location history (and any other stored user data for that matter) from the still affected services, but we (and I personally because my data is also on one of those sites) judge the risk of these vulnerabilities being exploited against live location tracking devices, much higher than the risk of historic data being exposed.”
As to the types of data being exposed, it includes: GPS coordinates, phone numbers, IMEI numbers, device information, and depending on which online service is being used, a hacker could even gain access to audio, video, and photos uploaded by the device being used.
While extremely convenient, these services do carry significant risks. Use them at your own risk.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 There’s a constant tug of war playing out on the national stage. On one side, privacy advocates are pushing for greater autonomy for end users, and hard limits to the types of searches that law enforcement agencies are allowed to conduct.
 Remember the KRACK WiFi (WPA2) vulnerability, discovered by Mathy Vanhoef? It turns out that his discovery was a catalyst for action. Recently, the WiFi Alliance, which is the industry’s standards organization, released details about its new WPA3 protocol.
 Have you been hearing strange, otherworldly sounds on your Bose or Sonos speakers? If so, rest assured that your speakers aren’t haunted. They’ve likely been hijacked by hackers.
 Another week, another attack vector, and this one deserves extra points for creativity.
 Facebook scams are fairly common occurrences, owing to the sheer size of the platform’s user base. It’s no surprise that there’s a new one making the rounds that you should be aware of.
 There’s some bad news if you own a computer driven by an Intel processor. Recently, a dangerous, catastrophic security flaw has been discovered in Intel’s X86-64 architecture that allows hackers to access the kernel, which sits at the heart of your OS. By accessing the kernel, a hacker can gain access to virtually everything on the targeted machine.
 Few things are more ubiquitous in an office environment than printers. Of course, these days, most printers are much more than simply that. They can also scan, copy and even send emails. As such, they’ve become an increasingly attractive option to hack, according to the latest data released by Barracuda Networks.
 SplashData has released their latest annual report on the most commonly used passwords. Unfortunately, the more things change, the more they stay the same.