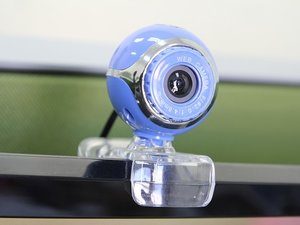
 Do you have a Mi-Cam in your home? Even if you don’t have kids, you may have one. They’re a highly popular, inexpensive means of keeping tabs on the comings and goings inside your home when you’re not around.
As with so many such devices these days, users have the option of installing either an Android or iOS app on their phones so they can peek in remotely, any time they like, and therein lies the problem.
It’s no secret that the IoT is filled with “smart” devices that don’t live up to their name when it comes to security, and the Mi-Cam is no exception. Security researchers have discovered that the communications between the company’s cloud servers where the video feeds live and the smartphones of the product’s user based are not secure.
So far, six different vulnerabilities have been identified, all of them critical. Any one of them would allow a hacker to hijack the window into your video feed and use that to scroll through literally every video feed on the company’s cloud, regardless of who owns it. All told, that’s more than fifty thousand video feeds, accessible from a single point of entry.
It gets worse. The attack is trivial to perform, because no SSL certificate is needed. All that’s required is a copy of either the Android or iOS mobile app.
The manufacturer of the Mi-Cam has been notified of these critical security flaws, but as of now, none have been addressed. The company has not released any information about when they might be. In light of that, if you have one, your best bet is to simply stop using it until the company can at least employ some rudimentary security protocols.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Depending on who you ask, Google’s Project Zero is either the thing that’s going to singlehandedly save the internet, or the bane of many companies’ existence. It’s easy to see both sides of the argument.
 Android users have a reason to cheer. According to the latest report by ESET, the number of ransomware attacks targeting Android devices declined in 2017. The decline represents a bit of an anomaly, given that in 2017, the most common type of malware attack (by a wide margin) was ransomware. Given that security researchers can’t name a particular reason for the decline, it’s important not to read too much into the data. Whether there are declining figures or not, ransomware attacks still played a prominent role in last year’s threat landscape across a whole spectrum of devices. This year is shaping up to be no different.
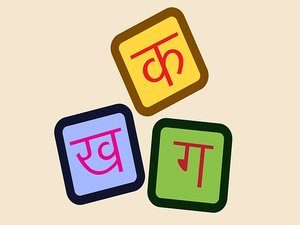 Recently, another “exotic character” bug was found in iOS. If someone sends this particular character (a special character that’s part of the Indian language pack) to your phone via any messaging app, it will not only crash your phone, but cause a variety of messaging apps to stop functioning.
 There’s a new strain of the “Rapid Ransomware” making the rounds, and because of how it’s being transmitted, it’s destined to have a higher than average rate of infection. The new strain was first discovered by Derek Knight. It is disturbing because it claims to come from the IRS, and will feature subject lines like “IRS Urgent Message-164.”
 Here’s a statistic that is as disturbing as it is frustrating. According to the latest “State of the Internet/Security” report for the fourth quarter of 2017, as published by Akamai, bot-traffic accounts for a staggering 43 percent of all login attempts. As bad as that figure is on its face, it’s far worse for companies in the hospitality industry, where the figure is an almost unbelievable 82 percent.
 Hackers are picky about their victims. They’ll target just about any group or organization, including the 2018 Olympics.
 Do you own a smart TV? More than half of all television sales in the US last year were smart TVs, so chances are decent that you own one. If you do, be aware that it may be collecting far more data about you than you think.
 Google is poised to make an important change to its Chrome browser beginning in July 2018.
 Image theft is one of the biggest problems on the internet. If you’re a photographer, you’ve almost certainly lost money because people find your work online and make a copy of it rather than paying for the right to use it.