
 There’s a new security threat to be worried about, and security professionals are warning that it could be very bad indeed. The new malware is known as the “Vega Stealer,” and is currently being used in a relatively simplistic phishing campaign designed to harvest financial data that has been saved in both Google Chrome and Firefox browsers. Unfortunately, based on an analysis of the code, it could be a much more serious threat.
Vega Stealer isn’t 100 percent original work, but rather, is a variant of another nasty bit of malware known as “August Stealer.” Built on the .NET framework, it’s designed to ferret out and steal cryptocurrency wallets, passwords, cookies, saved credit cards, and more.
If your computer is infected, and you’re using Firefox, Vega Stealer will specifically target the files “key3.db” and “key4.db,” along with “cookies.sqlite” and “logins.json,” which store a variety of keys and passwords.
In addition to that though, it can also take screen captures of your PC and scan for, and steal any file with the following extensions:
.xlsx
.xrft
.docx
.doc
Of course, it would be a trivial matter for the owners of the malware to expand this list even further.
As mentioned, the current campaign isn’t terribly sophisticated, relying on emails bearing titles like “Online Store Developer Required.” The emails being sent contain a poisoned file called “brief.doc” which contains macros designed to install the malware.
If the recipient clicks on the word doc, it will install a file named “ljoyoxu.pkzip” in that user’s “Music” directory, and then automatically executes the file so it can begin harvesting.
Researchers from Proofpoint, who found the malware strain had this to say:
“The document macro utilized in this campaign is a commodity macro that we believe is for sale and used by multiple actors, including the threat actor spreading Emotet banking Trojan. However, the URL pattern from which the macro retrieves the payload are the same as those used by an actor we are tracking who distributes the Ursnif banking Trojan, which often downloads secondary payloads such as Nymaim, Gootkit, or IcedID. As a result, we attribute this campaign to the same actor with medium confidence.”
Be on your guard.
 Depending on which side of the privacy debate you’re on, you’re either going to love or hate this announcement:
 Hulu recently announced that it would join both Netflix and Amazon Prime in allowing its users to download content to watch offline, but in Hulu’s case, it comes with a twist.
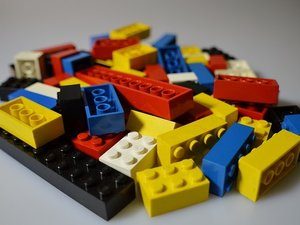 In terms of toys, what could possibly be better than LEGOS? How about LEGOS, combined with Alexa? That’s the latest idea from Amazon, who has paired the unlikely duo in a newly announced service called “LEGO Duplo Stories.” The new service (“skill,” in the parlance of Alexa) will be available on any device that offers Alexa support including Echo Dot and Amazon Echo. It provides a selection of stories with audio prompts that guide children in the construction of something with their LEGO Duplos that ties in with the story being told.
 Before Google released its Chrome browser, Firefox felt pretty good about their arrangement. They got a handsome reward in exchange for making Google.com their default search engine. It was a win-win.
 Microsoft has been having some “issues” of late. It’s April Windows 10 rollout had to be delayed on account of some mysterious BSOD (“Blue Screen of Death”) issues. This month’s rollout is plagued by similar problems, trading the BSOD issues for problems with both “Hey Cortana” and Google’s Chrome browser.
 At this year’s F8 Developer’s conference, Facebook announced a raft of changes and updates it will be rolling out later this year. Some are fun, others practical, but they’re all interesting. Here are the highlights:
 The Department of Health and Human services has issued a warning to healthcare providers to be on high alert for the SamSam strain of ransomware, which has been used to attack eight different health care entities so far this year.
 Twitter shot itself in the foot recently but is working hard to get out in front of the problem. According to a recent blog post, the company experienced an issue with its hashing routine – a process which masks user passwords, making them virtually impossible to crack.
 Apple promised that its iTunes app would be available on the Microsoft Store by the end of 2017. The announcement was greeted with enthusiasm, but unfortunately, the company didn’t meet their own deadline. They cited the need for more time to build a more robust user experience for Windows users.


