
 Microsoft recently made small but significant changes to its Office 365 subscription service and to OneDrive, which are often used in tandem. The goal is to make it easier for users whose files have been encrypted by ransomware (or otherwise corrupted) to recover them.
The most significant of the changes is a new button that Office 365 users will see a new “File Restore” function in both applications. If you’ve saved your Office 365 files to OneDrive, you’ll be able to restore files in a thirty-day window. In the event that your files are accidentally deleted or corrupted, getting them back is as simple as pressing the button and selecting the files to be restored.
That’s a huge win for Office 365 and OneDrive users, but there’s more.
The additional changes include:
A mobile alert sent to the phone number you select, which will inform you if your files may have been encrypted or otherwise tampered with
Support for end-to-end email encryption in their mail service (Outlook), including the web version of the mail app
Office now scans all links embedded in PowerPoint, Excel and Word documents to check if they point to malicious content on the web
All file attachments and links embedded in emails are now scanned for known phishing threats and viruses
Outlook.com now gives users the ability to prevent email recipients from forwarding your emails
The ability to password protect OneDrive shared links
That last one is also significant, and is a feature that OneDrive’s user base has been clamoring on about for quite some time. OneDrive has made it incredibly easy to share files via a link-based system, but unfortunately, never offered users a way to secure those links. That, thankfully, has now changed.
Individually, all these changes are quite good, but taken together, they represent a significant step in the right direction. Kudos to Microsoft for taking the threat of ransomware so seriously, and adding specific features to help protect their users.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Last year’s Wannacry attack was bad, but in many ways, it was a self-inflicted wound. According Webroot’s recently published “Annual Threat Report,” almost all of the machines that succumbed to the Wannacry attack were running Windows 7. That attack is estimated to have caused in excess of $4 billion in total losses.
 There’s a lot to talk about in Apple’s latest update to iOS. Version 11.3 boasts some significant changes and is well worth getting. We’ll go over the highlights below.
 If you use Amazon’s Cloud MP3 Locker to store your music online, now is the time to start looking for a new home for it. Last year, the company announced that they were ending the service, but didn’t provide a firm date. April 30, 2018 will be the last day you’ll be able to access your music if you don’t take action.
 There are some big changes coming to Facebook, which may have some serious unintended consequences.
 Another week, another high-profile data breach. This time, it’s Under Armour in the hot seat. Under Armour acquired the MyFitnessPal app back in February 2015, and the company recently announced that their new acquisition was hacked in late February 2018.
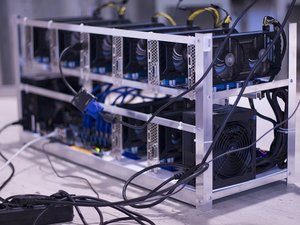 There’s a new type of hacking attack to be concerned with, and it’s growing by leaps and bounds. Called “Crypto-Jacking,” it’s a process by which malicious code is placed on websites. When the sites are visited, the code secretly siphons off a portion of the affected user’s PC, laptop, or smartphone’s processing power and uses it to mine for various cryptocurrencies so that the hackers can profit from it.
 If you are a fan of, and regularly use Goo.gl (the URL shortener service), brace for impact. The company has announced that as of March 30, 2019, the service will be shut down for good. Long before then, beginning April 18th of this year, only existing users will be able to shorten links via goo.gl. No new signups will be allowed.
 Researchers at Preempt Security recently discovered a critical flaw in Microsoft’s Credential Security Support Provider protocol (CredSSP for short) that impacts every version of Windows in existence. It could allow a hacker to remotely exploit Windows Remote Desktop to execute malicious code and steal any data stored on the machine.
 There’s a new threat on the horizon, according to security researchers from Check Point. A group of hackers in China are busy building a massive botnet that so far, totals almost five million Android smartphones. The hackers are quietly taking control of these devices using a strain of malware known as “RottenSys.”


