
 Gaming and Gambling are huge industries with a truly global footprint. It’s no surprise then, that these industries have become an increasingly popular target for hackers.
Interestingly, according to the latest report issued by ThreatMatrix, the attack vector of choice when it comes to these industries is IP Spoofing. It has increased by a staggering 257 percent since this time last year, making it far and away the fastest growing attack vector in the gambling and gaming industry.
A spokesman for ThreatMatrix had this to say about the report:
“Rising cybercrime levels is no small issue for a sector that enjoys a truly global customer base. With more than two billion gamers worldwide, nearly 60 percent of the industry’s traffic is cross-border.
Operators must contend with a rapidly evolving regulatory landscape and stringent new anti-money laundering laws, making the verification of the true location of a transacting gamer a vital component in authenticating identity.”
Note that at least some of the increase in IP spoofing stems from the gamers themselves, specifically in countries where certain gaming activities may be illegal. Gamers who wish to participate anyway, in violation of their country’s laws, have to fake an IP address to make it appear that they are located in some other country.
Another key finding of the report is the fact that an increasing percentage of gamers and gamblers access sites primarily from their mobile devices. Mobile access has increased by 45 percent between this year and last. As of now, fully 71 percent of gaming and gambling transactions are made on a mobile device, which is serving to make them an increasingly attractive target for hackers.
A TreatMatrix spokesman continues to explain, saying:
“To deal with these challenges, gaming and gambling operators must incorporate dynamic digital identity intelligence that pieces together key indicators such as device intelligence, true geolocation, online identity credentials and threat analysis to better inform risk decisions. The key is to be able to effectively differentiate trusted users from fraudsters and understand changes in trusted user behavior without adding unnecessary friction.”
A daunting challenge indeed.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
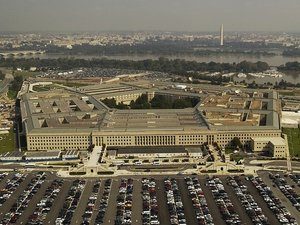 As many as 30,000 people made up of a mix of both civilian and military personnel have had their personal and financial information exposed. This exposure is what has been reported as a major security breach of the Pentagon.
 By now, almost everyone has heard of the Spectre and Meltdown security flaws that have been making headlines for more than a year. They’re serious flaws with dire implications for tens of millions of users around the world who have an intel-based PC.
 Facebook got hit hard by a currently unknown group of hackers. If you recently found yourself inexplicably logged out of the social media site, Facebook did it in response to the breach.
 Jose Rodriguez, a Spanish Apple enthusiast, has discovered a new security flaw to be aware of. He posted a Proof of Concept video showing the exploit in action.
 Symantec’s most recent statistics have revealed a disturbing trend. Malware designed to compromise checkout pages is seeing a big spike in use, with the company reporting a staggering 248,000 attempts since August 13th of this year, with more than a third of them (36 percent) between September 13th through September 20th. As disturbing as those numbers are, that’s just the tip of the iceberg.
 According to this year’s Traveler’s Risk Index, published by The Traveler’s Indemnity Company, a majority of business owners have a somewhat fatalistic view of hacking and data breaches.
 Firefox is upping the ante where digital security is concerned, having just announced the release of a new, free service called ‘Firefox Monitor.’ The new service is designed with one specific goal in mind: To assist users in finding out if their accounts were exposed via a data breach.
 If you use the GovPayNet portal, be advised that your personal information is currently at risk. Although at this point, there’s no indication that any hacker has made use of it. The portal is run by Government Payment Service, and is used by many Americans to pay fines, fees and bills generated by more than two thousand different government agencies operating in 35 states.
 Google is making a small but pivotal change as it relates to calls placed to 911 operators. Having recently finalized a complex partnership with RapidSOS and West (two emergency technology companies) and T-Mobile, Google will now send location data from its “Emergency Location Service” when an Android user places a 911 call.


