 Beware of compromised routers spreading malware. This is according to both Kaspersky Labs and a recently released government report.
Using hacked routers to spread malware is nothing new. Security insiders have known about it for years. However, since 2008, the number of instances where routers are being used to push malicious code has been steadily increasing. Researchers are observing marked increases in their use by APTs (Advanced Persistent Threat) around the world.
APTs are nothing new either, although their ranks have been growing in recent years. Many are state-sponsored hacking groups with virtually unlimited resources. Some are simply tight-knit groups of hackers banding together under a single banner.
Many people view hackers as lone wolves and that there are millions of lone wolves hacking networks across the globe. Increasingly though, these are becoming minor actors on the world stage. The real threat is now well-organized groups of hackers who can execute highly coordinated globe-spanning attacks and create botnets comprised of tens, or even hundreds of thousands, of compromised computers.
In addition to identifying and calling attention to a little-known attack vector, the recent announcement underscores an important weakness in current cybersecurity thinking. Most people are still laboring under the faulty assumption that they’re facing individual hackers operating out of a dark room in someone’s basement.
While those types of threats are no doubt present, it’s false to assume that’s where the biggest danger lies. If you get hacked, it’s just as likely (perhaps even more likely) that you’re actually facing a well-organized group who may have more resources at their disposal than your entire IT department. While you’re preparing to fight a skirmish, the barbarians are coming to your gates with an army. Most people are simply planning to fight the wrong type of battle, and that could prove to be a devastating mistake.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Last year’s Wannacry attack was bad, but in many ways, it was a self-inflicted wound. According Webroot’s recently published “Annual Threat Report,” almost all of the machines that succumbed to the Wannacry attack were running Windows 7. That attack is estimated to have caused in excess of $4 billion in total losses.
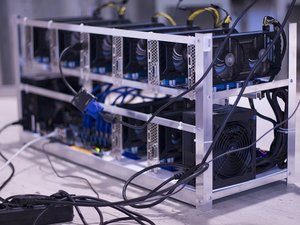 There’s a new type of hacking attack to be concerned with, and it’s growing by leaps and bounds. Called “Crypto-Jacking,” it’s a process by which malicious code is placed on websites. When the sites are visited, the code secretly siphons off a portion of the affected user’s PC, laptop, or smartphone’s processing power and uses it to mine for various cryptocurrencies so that the hackers can profit from it.
 There’s a new threat on the horizon, according to security researchers from Check Point. A group of hackers in China are busy building a massive botnet that so far, totals almost five million Android smartphones. The hackers are quietly taking control of these devices using a strain of malware known as “RottenSys.”
 According to a Microsoft security researcher, a massive malware attack attempted to install a cryptocurrency mining software on more than 400,000 computers in less than twelve hours. The failed campaign is noteworthy because of the attack vector used. It was a supply chain attack implemented by compromising Bittorrent, a highly popular program used to share and download files.
 If you post ads on Craigslist for short term employment, be aware that there’s a new malspam campaign that aims to distribute Sigma ransomware on the computers of unwary users.
 Hackers are picky about their victims. They’ll target just about any group or organization, including the 2018 Olympics.
 Sophos has released the results of their annual “State of Endpoint Security Today”, and it doesn’t paint a pretty picture. A full 54% of companies surveyed reported having been hit by a ransomware attack in 2017. Another 31% reported that they expect to be on the receiving end of such an attack in the near future.
 Google recently released their Play Store stats for 2017. The results are both encouraging and disheartening. Overall, Google caught and removed more than 700,000 malicious apps from the Play Store, minimizing their impact on the company’s massive Android user base.
 Do you play Blizzard online computer games such as World of Warcraft, Diablo III, Hearthstone, Starcraft II, or Overwatch? If so, there’s a potential problem you need to be aware of.