
 Another week, another new threat. This time, in the form of a new strain of malware that researchers are calling InvisiMole. The new threat was discovered by researchers at ESET, who found it on a number of hacked computers in Russia and the Ukraine.
While the researchers have yet to trace the software back to the group that developed it, based on the available evidence, the campaign appears to be tightly targeted and highly selective. Only a few dozen computers have been found to be infected, although all impacted systems are both high-profile and high-value.
As for the software itself, it’s a nasty piece of business capable of quietly taking control over an infected system’s video camera and capture audio. This allows them to both see and hear anything going on in the vicinity of the system. Essentially then, InvisiMole turns your computer into a compromised Amazon Echo.
Based on the sophisticated design of the software and the fact that the researchers have yet to be able to trace it back to the source, it’s believed that it has been developed by (or at least in partnership with) an unknown state actor. Although the current campaign is small and highly targeted, given its capabilities, InvisiMole could easily become a much more serious threat.
Even worse, it’s entirely possible that the original developers could lose control of the code, or that some other hacker group could reverse engineer it, causing it to spread far and wide.
Research into the software is still ongoing, and at this point ESET can’t say with certainty how the malicious payload is being delivered to target machines. Of course, at present, there is no antivirus software defense against it. Stay on your guard. You never know who might be watching.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Cyber-criminals around the world are increasingly focusing their attention on job seekers. According to the security firm Flashpoint, there has been a notable uptick in ploys involving phony job listings that attempt to get job seekers to give up personal information.
 Another week, another high-profile data breach, but this one can be filed under “Missed Opportunity.” The site in question is “TicketFly,” which is a web-based event ticket sales website owned by a company called Eventbrite. The TicketFly website was down since May 31st, and the normal homepage had been replaced by an image of Guy Fawkes with the message “Your Security Down I’m Not Sorry.”
 It seems like a new attack vector emerges on a weekly basis, and this week is no exception. The latest threat: Emails containing specialized audio files whose acoustic vibrations can damage your computer’s hard drive. This is possibly damaging to the point of causing system failure, data corruption, and making it impossible to successfully reboot your machine.
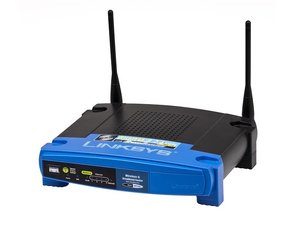 Cisco’s Talos Security Team has identified a new threat, and it’s a nasty one impacting more than half a million consumer-grade routers in the US. According to the Talos Team’s report, the new malware is impacting a broad cross-section of routers made by TP-Link, QNAP, Netgear, Mikrotik, and Linksys.
 An identity threat company called 4iQ has recently published a report called “Identities in the Wild: The Tsunami of Breached Identities Continues.” Unfortunately, the information in the report contains all bad news. Some of the details are simply confirmations of things we already knew, and some are shocking statistics that will leave you feeling dismayed.
 There’s a new security threat to be worried about, and security professionals are warning that it could be very bad indeed. The new malware is known as the “Vega Stealer,” and is currently being used in a relatively simplistic phishing campaign designed to harvest financial data that has been saved in both Google Chrome and Firefox browsers. Unfortunately, based on an analysis of the code, it could be a much more serious threat.
 Security researcher Assaf Baharav from Check Point Security has discovered a new twist on an old, fairly well-known attack. He was able to essentially “weaponize” PDFs to steal Windows credentials stored in NTLM hashes. Unfortunately, no action other than simply opening the PDF is required for the hacker to gain access to the information.
 Recently, a new strain of malware called “SquirtDanger” has been found by researchers at Palo Alto Networks Unit 42, and it’s a particularly nasty one for a couple of reasons. First and foremost, the owner of the malware isn’t orchestrating campaigns himself, but rather, selling his product as a commodity on the Dark Web.
 Score one for the good guys. A researcher from BrilliantIT was recently able to figure out how infected computers would connect to EITest’s command and control server, and using that information, was able to bring down their entire network.


