
 Microsoft is getting tough on so-called “registry cleaners”, and it’s about time. The company recently announced a planned change to Windows Defender (the anti-malware program that comes standard with every Windows installation). The change will see to the deletion of an increasing number of these registry cleaners. It’s a great move, and the company deserves credit for it, but there’s a catch. This type of software has been around for decades. So the move, as welcome as it is, comes very late in the game.
It’s overwhelmingly likely that you’ve seen these programs in action. They’re usually free downloads (though there are a few web based services too) that scan your system to find problems with your registry that the software claims are causing performance issues and slowing your machine down.
There are two major problems with this: First, the software tends to be light on details, refusing to provide much information about exactly why the “problems” that have been identified are impacting system performance. Worse, the software often incorrectly identifies critical system files and registry entries as being problematic. So of course, when they are deleted, they actually create many more problems than they solve.
Second, in order to actually fix the problems that have been identified, you’ve got to buy the premium version of the package. The result is that you’re losing money, and the software often breaks your system. Not a pretty picture.
This latest move by Microsoft builds on action they took back in 2016, when the company started penalizing the makers of such registry cleaners if their software didn’t provide adequate information. This missing information included why the problems they found needed to be fixed in the first place, and if they utilized a high pressure up-sell technique.
Ultimately, those moves proved to be insufficient, so Microsoft decided to take things to the next level. Now, they’re simply going to start deleting these no- or low-value programs. Late or not, that’s one less headache for you, and a very good thing.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Sophos has released the results of their annual “State of Endpoint Security Today”, and it doesn’t paint a pretty picture. A full 54% of companies surveyed reported having been hit by a ransomware attack in 2017. Another 31% reported that they expect to be on the receiving end of such an attack in the near future.
 Security researchers from around the web are reporting finding an increasing number of instances of proof of concept (PoC) code that incorporates the recently discovered Spectre and Meltdown vulnerabilities.
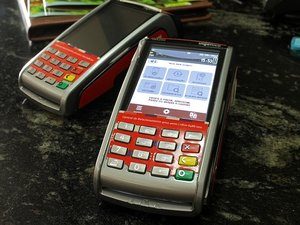 Oracle is currently the third-largest provider of POS (Point of Sale) software on the market today, which means that there’s a fairly good chance you’re using an Oracle POS system. If you are, there’s trouble ahead. A recently discovered security flaw could put your system at risk.
 Google recently released their Play Store stats for 2017. The results are both encouraging and disheartening. Overall, Google caught and removed more than 700,000 malicious apps from the Play Store, minimizing their impact on the company’s massive Android user base.
 Recently a critical flaw was found inside every Intel chip made during the last decade. The flaw makes two different exploits possible. These exploits have been dubbed “Meltdown” and “Spectre.”
 Do you play Blizzard online computer games such as World of Warcraft, Diablo III, Hearthstone, Starcraft II, or Overwatch? If so, there’s a potential problem you need to be aware of.
 By now, we’ve seen enough large-scale Point of Sale (POS) credit card thefts that patterns are beginning to emerge. Some companies follow the general arc of the narrative better than others and deserve credit for doing so, but in the end, the story is about the same.
 It’s official, the first macOS malware of 2018 is here. Discovered by an independent security researcher and dubbed “OSX/MaMi,” the code is functionally similar to DNSChanger malware.
 The ThreatMetrix Cybercrime Report 2017 is out, and is a troubling read for anyone who has anything to do with data security. As a fraud prevention company protecting nearly a billion and a half users around the world, they’re uniquely positioned to know, and their insights on the threat landscape is invaluable.


