
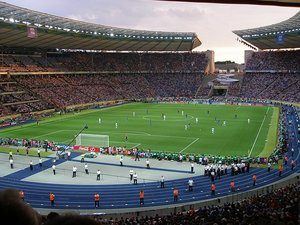
 According to the Kremlin, Russia prevented almost twenty five million cyber-attacks during the World Cup this year.
President Vladimir Putin praised the nation’s digital security forces by saying the following:
“I expect that your close and constructive interaction will continue and will contribute to ensuring the security of our states and our citizens in the future.”
Given the high-profile nature of the event, it was hardly a surprise that it would be a tempting target. In a survey by Lastline, in the weeks leading up to the World Cup, a staggering 72 percent of security professionals believed that an attack was likely.
The Russians took the threat seriously. In addition to beefing up their own security personnel, they also opened a “Cooperation Center” which was staffed by law enforcement officers from 34 different countries.
Some security professionals have cast doubt on the Kremlin’s figures, while others have at least unwillingly admitted that the figures weren’t out of the question.
David Grout (the Southern Europe Technical Director of FireEye) had this to say:
“Vladimir Putin’s statement that government security services have thwarted 25 million cyber-attacks linked to the FIFA World Cup may seem like a surprisingly high number, but not necessarily for those who work in the field. Every major event, whether sporting, political or otherwise, is likely to attract cyber-attacks. The 2018 World Cup is no exception. Before the competition had even started, there was evidence of Phishing attacks.
This included phishing attacks that started several weeks before the tournament and carried on throughout. These campaigns use several levers such as low-cost ticket offers, the chance to win a trip to Russia, promotions for items related to the World Cup (national team jerseys, mugs featuring players etc.). The main goal in this type of attack is to recover your banking information and force you to go through with the transaction to get the card number information, expiration date and also CCV.”
Even if the numbers are somewhat inflated, kudos to Russia for their deft handling of the event!

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 On May 14th, the Billings Clinic in Montana issued a breach notification statement, which explained that they detected unusual activity within one of its employee’s email accounts.
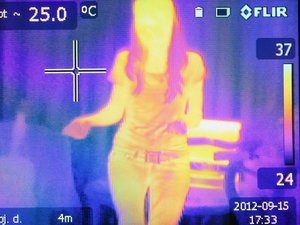 As if there weren’t enough ways for hackers to steal your passwords, now, there’s thermal imaging. If that sounds like something straight out of a science fiction movie, think again.
 Do you use Timehop? If you’re not sure what that is, it’s a popular, clever little app that reminds social media users about posts they’ve made in the past. It can be quite handy, especially if you’re active on numerous social media accounts.
 Researchers from the digital security firm ESET have recently spotted a new malware campaign with a nasty twist. It was created using a legitimate security certificate stolen from D-Link.
 Apple recently released an updated version of iOS, 11.4.1. They did so quietly, and without much fanfare, but the update includes one very powerful and exciting security update that’s deserving of special attention.
 There’s a lot to like about the contents of Adobe’s most recent “Patch Tuesday” update. It’s well worth downloading and installing, even if you normally take a pass on all but the most critical updates.
 It’s no secret that there are legions of scammers and spammers haunting the virtual halls of Facebook. As the world’s largest and most influential social networking site, it’s a natural target, making its masses of users natural targets, too.
 Internet security researcher Vinny Trola recently made a huge and disturbing discovery. A marketing firm called Exactis had left a massive database unsecured, allowing anyone who stumbled across it to access it.
 File this one away under “watch your permissions.” It’s recently come to light that an unknown number of third party apps have access to read emails sitting in your Gmail account.


