
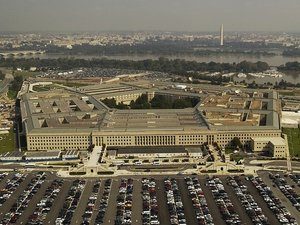
 As many as 30,000 people made up of a mix of both civilian and military personnel have had their personal and financial information exposed. This exposure is what has been reported as a major security breach of the Pentagon.
This is proof positive that no organization is safe from watchful hackers scattered all around the world.
The Associated Press report on the incident includes:
“The department is continuing to gather additional information about the incident, which involves the potential compromise of Personally Identifiable Information (PII) of DoD personnel maintained by a single commercial vendor that provided travel management services to the department. This vendor was performing a small percentage of the overall travel management services of the DoD…The department is continuing to assess the risk of harm and will ensure notifications are made to affected personnel.”
While there’s no good time for a data breach like this, it couldn’t have come at a worse time. The Government Accountability Office (GAO) had issued a scathing report of critical vulnerabilities in virtually all of the weapons systems programs the agency currently runs.
A small excerpt of the report reads as follows:
“One test report indicated that the test team was able to guess an administrator password in nine seconds…Multiple weapon systems used commercial or open source software, but did not change the default password when the software was installed, which allowed test teams to look up the password on the internet and gain administrator privileges for that software.”
It gets worse. When confronted with the findings of the report, Pentagon officials dismissed the report as being unrealistic.
Clearly, there was something to the report, or this breach would not have happened. The hope is that it will be sufficient to cause Pentagon officials to do some soul searching and reevaluate their positions. If not, you can bet that something like this will happen again.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Microsoft is having problems, and those problems are spilling out onto the company’s massive user base. In a highly unusual move, the company pulled its latest Windows 10 update after receiving numerous complaints from users about missing files.
 Most people don’t know what the latest version of WiFi is called. That’s the fault of the Wi-Fi Alliance, the group that manages the implementation of WiFi. Since their earliest days, the group has insisted on a highly unconventional version numbering scheme.
 Facebook got hit hard by a currently unknown group of hackers. If you recently found yourself inexplicably logged out of the social media site, Facebook did it in response to the breach.
 Jose Rodriguez, a Spanish Apple enthusiast, has discovered a new security flaw to be aware of. He posted a Proof of Concept video showing the exploit in action.
 Change is coming to the way Microsoft handles search across its ecosystem. If you use the home edition of Office, you’re not likely to notice, but if you use Office 365, the changes will be significant.
 If you’re one of the relatively few people who use Google+ in something other than an Enterprise setting, be advised that the clock is ticking. Google has just announced that they’re sunsetting the service. It will be going offline for consumers at some point over the next ten months.
 Symantec’s most recent statistics have revealed a disturbing trend. Malware designed to compromise checkout pages is seeing a big spike in use, with the company reporting a staggering 248,000 attempts since August 13th of this year, with more than a third of them (36 percent) between September 13th through September 20th. As disturbing as those numbers are, that’s just the tip of the iceberg.
 Windows 10 is far and away the fastest growing version of the OS in the company’s history. It recently hit an installation base of a staggering 700 million devices after about three years on the market.
 If you use the GovPayNet portal, be advised that your personal information is currently at risk. Although at this point, there’s no indication that any hacker has made use of it. The portal is run by Government Payment Service, and is used by many Americans to pay fines, fees and bills generated by more than two thousand different government agencies operating in 35 states.


