
 Gaming and Gambling are huge industries with a truly global footprint. It’s no surprise then, that these industries have become an increasingly popular target for hackers.
Interestingly, according to the latest report issued by ThreatMatrix, the attack vector of choice when it comes to these industries is IP Spoofing. It has increased by a staggering 257 percent since this time last year, making it far and away the fastest growing attack vector in the gambling and gaming industry.
A spokesman for ThreatMatrix had this to say about the report:
“Rising cybercrime levels is no small issue for a sector that enjoys a truly global customer base. With more than two billion gamers worldwide, nearly 60 percent of the industry’s traffic is cross-border.
Operators must contend with a rapidly evolving regulatory landscape and stringent new anti-money laundering laws, making the verification of the true location of a transacting gamer a vital component in authenticating identity.”
Note that at least some of the increase in IP spoofing stems from the gamers themselves, specifically in countries where certain gaming activities may be illegal. Gamers who wish to participate anyway, in violation of their country’s laws, have to fake an IP address to make it appear that they are located in some other country.
Another key finding of the report is the fact that an increasing percentage of gamers and gamblers access sites primarily from their mobile devices. Mobile access has increased by 45 percent between this year and last. As of now, fully 71 percent of gaming and gambling transactions are made on a mobile device, which is serving to make them an increasingly attractive target for hackers.
A TreatMatrix spokesman continues to explain, saying:
“To deal with these challenges, gaming and gambling operators must incorporate dynamic digital identity intelligence that pieces together key indicators such as device intelligence, true geolocation, online identity credentials and threat analysis to better inform risk decisions. The key is to be able to effectively differentiate trusted users from fraudsters and understand changes in trusted user behavior without adding unnecessary friction.”
A daunting challenge indeed.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 This hasn’t been a great month for two of the titans of tech. Both Apple and Microsoft have been plagued with bug-riddled updates to their operating systems. In Apple’s case, their new iOS 12 had to be patched just three weeks after its release because of all the bugs the company’s burgeoning user base discovered almost immediately after updating.
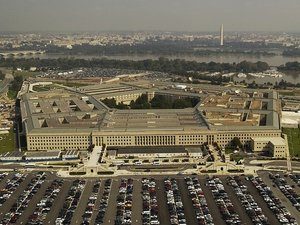 As many as 30,000 people made up of a mix of both civilian and military personnel have had their personal and financial information exposed. This exposure is what has been reported as a major security breach of the Pentagon.
 Microsoft is having problems, and those problems are spilling out onto the company’s massive user base. In a highly unusual move, the company pulled its latest Windows 10 update after receiving numerous complaints from users about missing files.
 Most people don’t know what the latest version of WiFi is called. That’s the fault of the Wi-Fi Alliance, the group that manages the implementation of WiFi. Since their earliest days, the group has insisted on a highly unconventional version numbering scheme.
 By now, almost everyone has heard of the Spectre and Meltdown security flaws that have been making headlines for more than a year. They’re serious flaws with dire implications for tens of millions of users around the world who have an intel-based PC.
 Facebook got hit hard by a currently unknown group of hackers. If you recently found yourself inexplicably logged out of the social media site, Facebook did it in response to the breach.
 Change is coming to the way Microsoft handles search across its ecosystem. If you use the home edition of Office, you’re not likely to notice, but if you use Office 365, the changes will be significant.
 If you’re one of the relatively few people who use Google+ in something other than an Enterprise setting, be advised that the clock is ticking. Google has just announced that they’re sunsetting the service. It will be going offline for consumers at some point over the next ten months.
 Symantec’s most recent statistics have revealed a disturbing trend. Malware designed to compromise checkout pages is seeing a big spike in use, with the company reporting a staggering 248,000 attempts since August 13th of this year, with more than a third of them (36 percent) between September 13th through September 20th. As disturbing as those numbers are, that’s just the tip of the iceberg.


