
 By now, you’ve almost certainly heard of “Spectre,” one of two recently discovered security flaws that impact every chip made by Intel in the last ten years.
The story of Spectre, and Intel’s response to it has been an interesting one. In response to the flaw’s discovery, Intel rushed a firmware patch, but quickly had to take it back and recommend that users not install it, because it created as many problems as it solved.
Intel has since released a better, more stable patch, but hasn’t stopped there. The company recently revealed that it is introducing various hardware protections against Spectre-like vulnerabilities that may be detected in the future.
According to Intel’s CEO, Brian Krzanich, “(We have) redesigned parts of the processor to introduce new levels of protection through partitioning. As we bring these new products to market, ensuring that they deliver the performance improvements people expect from us is critical. Our goal is to offer not only the best performance, but also the best secure performance.”
While that is welcome news for people planning to make purchases in the near future, owners of existing Intel-powered equipment will still have to have to rely on firmware updates for Spectre protection. This unfortunately comes with the tradeoff of a hit to CPU performance.
In tandem with that update, the company also announced that as of now, they have firmware updates available for all of its products launched within the last five years. This coupled with their recent partnership with Microsoft to help deliver Spectre updates to their legions of impacted customers should provide peace of mind, even with the expected hits to system performance.
Unfortunately, with new variants of Spectre and Meltdown being discovered on a regular basis, this is likely not the last we’ll hear about this issue.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 According to a Microsoft security researcher, a massive malware attack attempted to install a cryptocurrency mining software on more than 400,000 computers in less than twelve hours. The failed campaign is noteworthy because of the attack vector used. It was a supply chain attack implemented by compromising Bittorrent, a highly popular program used to share and download files.
 If your company has an incident response plan that you can rely on in the face of a cyber attack, then you’re ahead of most of the world, according to research recently conducted by the Ponemon Institute. Shockingly, more than 75 percent of survey respondents from around the world admitted that they have no formal incident response plan. Even worse, half of the companies that indicated they had an incident response plan said that it was informal.
 According to a new report published by Spiceworks, nearly 90 percent of businesses will use some type of biometric technology for authentication by the year 2020. In fact, some 62 percent of companies already use biometrics in some form, with another 24 percent stating their intention to do so within the next two years.
 The “Spectre” vulnerability that impacts literally every Intel chip made over the last decade keeps finding new ways to make the news. In this instance, researchers at Ohio State University have discovered a new variant of the vulnerability that they have dubbed “SGX Spectre.” To understand how it’s different, a bit of explanation is in order.
 It looks like it’s going to be another bad month for Equifax. The company just can’t seem to get out of its own way.
 Do you have a Mi-Cam in your home? Even if you don’t have kids, you may have one. They’re a highly popular, inexpensive means of keeping tabs on the comings and goings inside your home when you’re not around.
 Depending on who you ask, Google’s Project Zero is either the thing that’s going to singlehandedly save the internet, or the bane of many companies’ existence. It’s easy to see both sides of the argument.
 Android users have a reason to cheer. According to the latest report by ESET, the number of ransomware attacks targeting Android devices declined in 2017. The decline represents a bit of an anomaly, given that in 2017, the most common type of malware attack (by a wide margin) was ransomware. Given that security researchers can’t name a particular reason for the decline, it’s important not to read too much into the data. Whether there are declining figures or not, ransomware attacks still played a prominent role in last year’s threat landscape across a whole spectrum of devices. This year is shaping up to be no different.
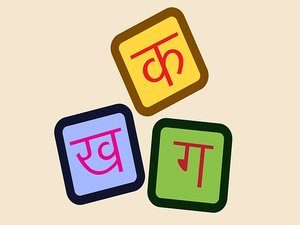 Recently, another “exotic character” bug was found in iOS. If someone sends this particular character (a special character that’s part of the Indian language pack) to your phone via any messaging app, it will not only crash your phone, but cause a variety of messaging apps to stop functioning.


