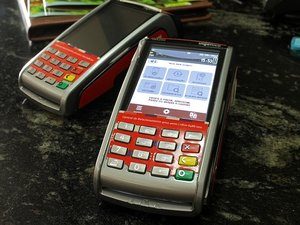
 Oracle is currently the third-largest provider of POS (Point of Sale) software on the market today, which means that there’s a fairly good chance you’re using an Oracle POS system. If you are, there’s trouble ahead. A recently discovered security flaw could put your system at risk.
Oracle has already identified and patched the security flaw, but there’s a problem. Since POS systems are deemed “mission critical” by most businesses, System Administrators rarely schedule maintenance for them on fears that an unstable patch or update could cause undue downtime for the company. Because of that, it will likely be a month or more before the new update finds its way to all 300,000 of the at-risk systems.
As security flaws go, this one is fairly nasty, too, as it allows a hacker to collect configuration files from any vulnerable Micros POS system. This data can then be used to grant the hacker full, unrestricted access to the POS system, as well as the database and server it feeds information to.
Most hackers attacking a POS would be content with simply collecting credit card details for resale on the Dark Web However, with this exploit, any sort of malware could be installed to use against the company later.
Even worse, a hacker need not be in close proximity to the device in question. A carefully crafted HTTP request could trigger the security flaw and open the door. Of course, if a hacker is in close proximity to the system, then there are many easier ways to infect it. One only needs to distract the sales clerk long enough to attach a simple Raspberry Pi board equipped to run the exploit code and the damage is done.
The bottom line is, if you use an Oracle POS, make installing the latest security patch a priority. You’ll be vulnerable until you do.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Google recently released their Play Store stats for 2017. The results are both encouraging and disheartening. Overall, Google caught and removed more than 700,000 malicious apps from the Play Store, minimizing their impact on the company’s massive Android user base.
 Recently a critical flaw was found inside every Intel chip made during the last decade. The flaw makes two different exploits possible. These exploits have been dubbed “Meltdown” and “Spectre.”
 Do you play Blizzard online computer games such as World of Warcraft, Diablo III, Hearthstone, Starcraft II, or Overwatch? If so, there’s a potential problem you need to be aware of.
 By now, we’ve seen enough large-scale Point of Sale (POS) credit card thefts that patterns are beginning to emerge. Some companies follow the general arc of the narrative better than others and deserve credit for doing so, but in the end, the story is about the same.
 It’s official, the first macOS malware of 2018 is here. Discovered by an independent security researcher and dubbed “OSX/MaMi,” the code is functionally similar to DNSChanger malware.
 The ThreatMetrix Cybercrime Report 2017 is out, and is a troubling read for anyone who has anything to do with data security. As a fraud prevention company protecting nearly a billion and a half users around the world, they’re uniquely positioned to know, and their insights on the threat landscape is invaluable.
 Intel’s year isn’t getting off to a very good start. Just after the discovery of a pair of critical vulnerabilities that have been in their chipsets for more than a decade comes the discovery of yet another serious flaw that could impact millions of laptops around the world.
 Normally, Google’s robust series of checks and audits are pretty good at catching malicious code and preventing it from making its way to the Play Store. Sometimes, however, something slips through anyway despite the company’s best efforts. This latest one is particularly bad.