
 You probably haven’t heard of the Centers for Medicare and Medicaid Systems.
They’re a low-profile division of the Department of Health and Human Services responsible for administering the Affordable Care Act.
Recently, the company announced that they detected anomalous activity in the systems related to the healthcare.gov website that brokers and insurance agents use to assist people who apply for healthcare coverage.
The abnormal activity was detected in the Federally Facilitated Exchange system, and the direct enrollment pathway in particular. This is connected to (but separate from) the healthcare.gov website itself.
A statement issued by the Centers for Medicare and Medicaid Systems said:
“At this time, we believe that approximately 75,000 individuals’ files were accessed. While this is a small fraction of the consumer records present on the FFE, any breach of our system is unacceptable… We will continue to work around the clock to help those potentially impacted and ensure the protection of consumer information.”
CMS made it clear that their investigation into the matter was still in its earliest stages.
They did offer the following additional information:
“Upon verification of the breach, CMS took immediate steps to secure the system and consumer information, further investigate the incident, and subsequently notify federal law enforcement. We are actively engaged in and committed to helping those potentially impacted as well as ensuring the protection of consumer information.”
Additionally, CMS stated that they identified the broker accounts that were associated with the anomalous activity and deactivated them out of an abundance of caution.
At some point in the near future, we can expect that CMS will be contacting those whose data was compromised and providing them with a series of next steps. The agency is already moving to bolster their security measures and promises that they’ll have them in place before the end of October 2018.
If you’ve used the healthcare.gov portal and required the assistance of a broker or insurance agent to get coverage for yourself and your family, there is a small chance your data may have been compromised. However, at this point, there’s no way to be certain. Be on the lookout for a communication from CMS in the near future, however, just in case.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Microsoft hasn’t been terribly impressive lately when it comes to Windows 10 updates. In fact, it’s fair to say that they’ve been a complete mess. Just recently, they’ve issued updates that have deleted user files and caused crashes after creating incompatibilities with keyboard drivers. Now, (courtesy of the most recent Windows 10 update), many users are reporting that they’ve got no sound due to corrupted or incompatible audio drivers.
 Google is taking additional steps to bolster user privacy and better secure the data of the company’s legions of Android device owners. The company recently announced a change to the Android Backup Service that will encrypt all user backup data stored on its cloud servers, such that even Google itself can’t read it.
 Gamers take the games they play seriously. So seriously, in fact, that they’re not above resorting to dirty tricks to score a win.
 Gaming and Gambling are huge industries with a truly global footprint. It’s no surprise then, that these industries have become an increasingly popular target for hackers.
 This hasn’t been a great month for two of the titans of tech. Both Apple and Microsoft have been plagued with bug-riddled updates to their operating systems. In Apple’s case, their new iOS 12 had to be patched just three weeks after its release because of all the bugs the company’s burgeoning user base discovered almost immediately after updating.
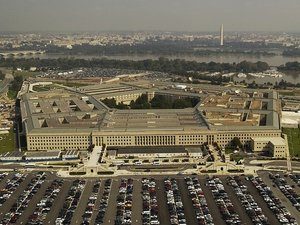 As many as 30,000 people made up of a mix of both civilian and military personnel have had their personal and financial information exposed. This exposure is what has been reported as a major security breach of the Pentagon.
 Microsoft is having problems, and those problems are spilling out onto the company’s massive user base. In a highly unusual move, the company pulled its latest Windows 10 update after receiving numerous complaints from users about missing files.
 Most people don’t know what the latest version of WiFi is called. That’s the fault of the Wi-Fi Alliance, the group that manages the implementation of WiFi. Since their earliest days, the group has insisted on a highly unconventional version numbering scheme.
 By now, almost everyone has heard of the Spectre and Meltdown security flaws that have been making headlines for more than a year. They’re serious flaws with dire implications for tens of millions of users around the world who have an intel-based PC.


