
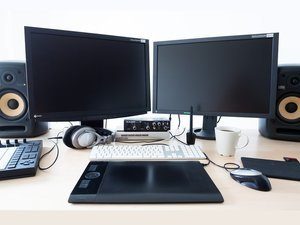
 It may sound like something straight out of a science fiction movie, but recently, researchers have made a disturbing discovery. Using nothing more than an off-the-shelf microphone, it’s possible for an attacker to determine what content you’re viewing on your computer monitor.
The researchers tested a variety of LCD screens (with both LED and CCFL backlighting) and observed that the high-pitched noise made by the monitors changed as the content displayed on the screen changed.
The research team tested a variety of methods of recording audio data from the monitors in question, and found that they could capture sufficient data with a few methods. First, a smartphone positioned near the screen, second a compromised smart virtual assistant (like Google Home or Amazon’s Alexa), and third, using a parabolic microphone from up to ten meters distant.
Even more disturbing, the researchers discovered that an attacker could correctly identify the website a victim was looking at with up to 97 percent accuracy if the microphone was close to the monitor, and with 90.9 percent accuracy with microphones placed at some distance.
Worst of all, subtle changes in the pitch of your display screen make it possible for hackers to identify what specific characters are being displayed with an accuracy that ranged from 88 percent (more distant microphones) to 98 percent (microphones in close proximity to the monitor). This makes it entirely possible to glean passwords and other sensitive information.
Granted, this is an extremely exotic form of attack that requires a great deal of advance preparation by the attacker. Because of this, it’s unlikely that it will see widespread use anytime soon. Even so, it’s something that a careful and determined hacker could do right now using off the shelf technology, and there’s very little the victim could do to prevent it.
While we’re unlikely to see equipment manufacturers take the necessary steps to mask acoustic emanations, robust on-site physical security measures would make detection of this type of attack fairly easy.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Telecommunications giant T-Mobile is the latest victim of a large-scale data breach, with personal data belonging to more than two million of its customers having been leaked. The exposed information included customer name, phone number, email address, billing zip code, account number and whether the account was pre-paid or post-paid.
 Android users have a new threat to contend with, according to a sixteen-page whitepaper outlining a new malware strain.
 Google has introduced a new Gmail feature called “Confidential Mode,” which seeks to make sending and receiving important or sensitive emails more secure. Unfortunately, it may have inadvertently created as many problems as it solves.
 Do you use Photoshop? Does anyone who works for you use it? If so, you’ll want to apply the latest security patch immediately.
 Intel has had a tough time of things so far this year. The most recent trouble stems from yet another newly discovered security flaw in the company’s processors, bearing the inelegant name of “L1 Terminal Fault,” or “Foreshadow” by those who have discovered it.
 Nothing bad could possibly happen to your company’s network if the only piece of information the hackers have is your fax number, right?
 How seriously does the average consumer take data theft? It’s an interesting (and fair) question, and one that Radware recently attempted to answer when the company sent out surveys. They contacted more than three thousand people to conduct its recent survey titled “Consumer Sentiments: Cybersecurity, Personal Data and the Impact on Customer Loyalty.”
 These days, we expect giant corporations, government agencies and medical facilities to be the targets of hackers. However, golf is something new.


