
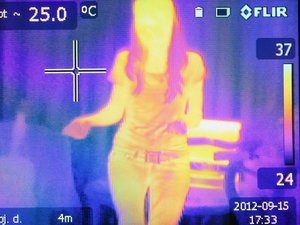
 As if there weren’t enough ways for hackers to steal your passwords, now, there’s thermal imaging. If that sounds like something straight out of a science fiction movie, think again.
Researchers from the University of California at Irvine recently discovered and demonstrated a technique that involves the use of a thermal imaging camera to capture heat traces left by human fingertips as they type passwords into a keyboard. In fact, their technique is effective for up to thirty seconds after the user removes his hands from the keyboard.
Per the researchers, “Although thermal residue dissipates over time, there is always a certain time window during which thermal energy readings can be harvested from input devices to recover recently entered, and potentially sensitive information.”
The team tested their technique using off the shelf technologies, and on four different keyboards. Their findings indicated that a full password could be obtained by scanning for thermal residues on those keyboards, provided that the scan was taken within thirty seconds of the first key being pressed. After a full minute, it was still possible to obtain partial passwords.
They used an FLIR camera on a tripod set two feet from the keyboards being tested, and the results of their findings were published in a paper called simply, “Thermanator.”
FLIR makes a number of different camera models that can capture heat. Their most basic model, the FLIR One Pro is a $400 accessory available as a smartphone attachment. Some phones (like the CAT S61) ship with the FLIR module embedded in the technology.
The team noted that the ease with which a password could be detected in this manner had a lot to do with the typing style of the target being monitored. Passwords entered by “hunt and peck” typists could be gleaned between 19.5 and 31 seconds, while passwords entered by touch typists took upwards of 50 seconds to be gleaned.
Obviously, this is a fairly exotic form of attack. Although it utilizes off the shelf technology, it would require an extraordinary level of access to set the equipment up, and an extraordinary lack of vigilance on the part of security personnel not to detect the equipment in relatively short order. Even so, it’s certainly within the realm of possibility, and one more thing to be on guard against.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Do you use Timehop? If you’re not sure what that is, it’s a popular, clever little app that reminds social media users about posts they’ve made in the past. It can be quite handy, especially if you’re active on numerous social media accounts.
 Researchers from the digital security firm ESET have recently spotted a new malware campaign with a nasty twist. It was created using a legitimate security certificate stolen from D-Link.
 Internet security researcher Vinny Trola recently made a huge and disturbing discovery. A marketing firm called Exactis had left a massive database unsecured, allowing anyone who stumbled across it to access it.
 While a significant percentage of Americans are suspicious of government spending beyond the essentials, there’s at least one notable exception, according to a recent survey conducted by SecurityFirst.
 Another week, another high-profile data breach. This time, Adidas and their online store was the target.
 Researchers from Ruhr-Universität Bochum and New York University in Abu Dhabi have discovered serious security flaws in 4G LTE networks that allow hackers to spy on, listen in on, intercept, and disrupt phone calls and text messages.
 Menlo Security has recently published a new report that will probably dismay you if you’re a business owner.
 Researchers at Okta Security have stumbled across something big. Recently, they discovered a flaw in Apple’s OS that would have allowed hackers to completely undermine Apple’s code signing process.
 Do you use Cortana? It’s a handy virtual assistant (like Siri) built into Windows 10. Unfortunately, as useful as she is, there’s a problem. Even if you don’t use Cortana yourself, take heed: Microsoft has recently issued a security update based on findings by McAfee researchers.


