
 If you use the GovPayNet portal, be advised that your personal information is currently at risk. Although at this point, there’s no indication that any hacker has made use of it. The portal is run by Government Payment Service, and is used by many Americans to pay fines, fees and bills generated by more than two thousand different government agencies operating in 35 states.
Unfortunately, the way the website is configured, when it issues a receipt for a payment, it numbers those receipts sequentially. All a hacker would have to do would be to change the receipt number in the URL to see any previous receipts, and all of the information it contains.
When the flaw was discovered by journalist Brian Krebs, more than fourteen million old records were exposed in this manner. He contacted Government Payment Service to inform them of the flaw, and the agency moved quickly to address the issue. They said in a formal statement that they “did not adequately restrict access to only authorized recipients.”
They went on to assure their users that there’s no indication that any data had been improperly accessed. They added that the receipts generated don’t include any information that could be used by a hacker to initiate any type of financial transaction.
Unfortunately, the reality was a bit different. The receipts contain the names, addresses and phone numbers of the person paying the fee in question, along with the last four digits of whatever credit or debit card was used to make payment. That is more than enough information to enable a hacker to initiate a phishing attack to get the rest.
Nick Bilorgoskiy of Juniper Networks had this to say about the matter:
“Online payment providers…should take special care to protect their customers’ receipts by using HTTPS and checking that the user is logged in and has permissions to view them. To avoid information disclosure and directory traversal issues, I also recommend denying anonymous web visitors the ability to read permissions for any unnecessary files from web-accessible directories.”
It’s good advice, and here’s hoping that Government Payment Service will take it. If you use the service, there’s nothing for you to do. You don’t need to change your password, since it was never exposed. Just be mindful that someone may have seen any data your receipts contain before the site was secured.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 A new piece of legislation is making its way through the halls of Congress that could standardize and streamline the data security and breach notification process for financial institutions. This is something that most people in the industry tout as an improvement over the current situation.
 Western Digital has a big problem, and if you use the company’s “My Cloud” network-attached storage (NAS) storage devices, you’ve got one too. The WD My Cloud service is enormously popular because it’s so convenient, allowing both business owners and individuals to store their files, perform periodic backups, and of course, access their data from anywhere in the world.
 We’ve known for some time now that the next big crisis the internet will have to come to grips with is the dramatic rise of the Internet of Things (IOT).
 There’s a new report out, authored by ProofPoint, and its findings for business are grim.
 Perhaps the most significant change to the browser is the addition of a new password manager, which will offer to generate a random password when you sign into a website for the first time. The randomly generated password will be securely tucked away inside your Google Account and synced across both desktop and mobile versions of Chrome.
 The Internet on devices continues to be a major problem when it comes to security. Unfortunately, a big part of the reason why comes down to end users. Recently, Bitdefender released a new report entitled “The IoT Threat Landscape And Top Smart Home Vulnerabilities in 2018,” and it paints a grim picture indeed.
 Do you use the Chrome browser extension for the MEGA file storage service? If you do, please read this article carefully. The official extension for that service has been compromised. It has been replaced with a malware version that has the capability to steal user login data for a number of popular websites, including Github, Google, Amazon, Microsoft and more.
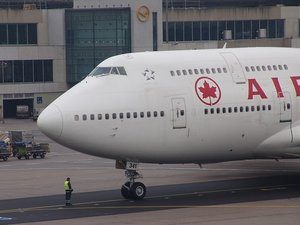 If you fly Air Canada and use their mobile app, it may be time to change your password. The company recently announced that between August 22nd and August 24th of this year, they detected “unusual log-in behavior,” and that a small fraction (some 20,000) of their 1.7 mobile app users may have had their data compromised as a result.
 Tech Support scams are nothing new, but they are getting increasingly sophisticated. Worse, tech giants like Google are finding it notoriously difficult to detect them.


