
 A dark day for Lifelock, the Identity Theft Protection company. It has recently come to light that the company may have accidentally exposed their customers to additional attacks.
They recently fixed a vulnerability on their website that allowed anyone with a browser to index email addresses associated with their entire customer database. The vulnerability can even unsubscribe users from company communications designed to keep them safe and keep them apprised of changes they need to be aware of.
In addition to that, the vulnerability made it possible for hackers to initiate highly targeted phishing campaigns and create a convincing spoof of the Lifelock brand.
Symantec, which purchased Lifelock in late 2016, took the company’s website offline not long after being contacted by KrebsOnSecurity, which is how they became aware of the vulnerability.
Krebs was made aware of it by Nathan Reese, a freelance security consultant based out of Atlanta. Nathan put together a proof of concept script that was capable of downloading the email addresses of all 4.5 million of Lifelock’s customers and then presented it to Krebs.
Reece aborted his script after downloading 70 emails so as not to set off alarm bells at Lifelock, and had this to say about his discovery:
“If I were a bad guy, I would definitely target your customers with a phishing attack because I know two things about them. That they’re a LifeLock customer and that I have those customers’ email addresses. That’s a pretty sharp spear for my spear phishing right there. Plus, I definitely think the target market of LifeLock is someone who is easily spooked by the specter of cybercrime.”
He’s not wrong, so it’s good that Reece isn’t a bad guy.
There’s no evidence that any hackers were aware of the issue, or made off with any of Lifelock’s customer emails. However, given the existence of the now-patched flaw, it pays to be suspicious of any email that appears to be coming from Lifelock for the short to medium term, at least.

President & CEO
I hope you enjoyed this article. My mission is to take your stress away from dealing with IT problems. Call (252) 565-1235 or send me a message at our contact us page if you have a question, comment or want help.
 Microsoft has made numerous ventures into the smartphone ecosystem, but so far, they’ve only been met with limited success. This time, they’re trying something a little different.
 Twitter has long had a reputation for being at the mercy of bots that have been used to sway public discourse and opinion.
 If you’ve used Windows 10 for any length of time, you’ve probably had this happen to you. You’re right in the middle of working on something important, and all of a sudden, your OS decides it would be a great time to install some updates!
 Mimecast’s 2018 “State of Email Security” report is out, and although it’s contents are hardly a surprise, the news it contains is mostly bad.
 There is a small but significant change from Google, with the release of Chrome 68. The updated browser will now prominently notify browsers when they surf their way to non-HTTPS websites, displaying them as “Not Secure.”
 There’s a new Bluetooth security vulnerability to be aware of, tracked as CVE-2018-5383, and it’s a nasty one.
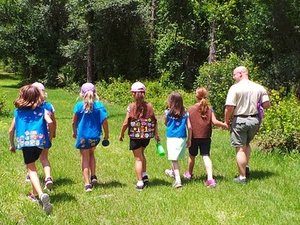 The girl scouts have officially moved into the 21st century.
 If you’re like most people, you probably rely heavily on the GPS function of your phone. Type in an address and your phone helpfully guides you, turn by turn, to your destination. It’s one of the most often utilized features of a smartphone, and of course, the hackers are very interested in interfering with it.
 Positive Technologies has just released a new report that paints a grim picture for IT professionals. If your sense is that the number of cyberattacks are increasing, you’re not wrong. In fact, it’s probably worse than you realize.


