
 For hackers around the world, success breeds more success, it seems.
A company called KnowBe4 has released a report entitled “Top Ten Global Phishing Email Subject Lines For Q3 2017.” To prepare it, they analyzed email subject lines from simulated phishing tests to determine what the most effective approach was.
Their findings were that “Official Data Breach Notification” was the hands-down winner, generating far more click-throughs than any other.
Perry Carpenter, KnowBe4’s Chief Evangelist, and Strategy Officer had this to say about the report:
“Phishing attacks are responsible for more than 90% of successful cyber-attacks and the level of sophistication hackers are now using makes it nearly impossible for a piece of technology to keep an organization protected against social engineering threats.
We see urgency and fear of a breach as the drivers. We have over 1400 templates and a concentration of themes so we know what is highly effective. Phishing attacks are smart, personalized and timed to match topical news cycles. Businesses have a responsibility to their employees, their shareholders, and their clients to prevent phishing schemes.”
Wise words and the first step on the path to prevention is knowing what triggers are the most effective, which makes the KnowBe4 report especially valuable to data security teams, regardless of what business your company is in.
The irony, however, is inescapable.
The reason that “Official Data Breach Notification” is such a devastatingly effective phishing headline is simply that the hackers have been devastatingly effective. Barely a day goes by that we are not greeted by some grim headline and a news story recounting the woes of yet another company suffering from yet another massive breach resulting in hundreds of thousands, millions, or more consumer data files stolen.
They are, in a very real sense, leveraging the power of their own success to become even more successful, and that’s sadly not likely to change anytime soon.
 Hackers around the world are continuing to innovate at a terrifying, relentless pace, and that truth is reflected in the latest form of ransomware to be found in the wild.
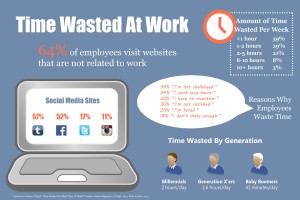 can choose which websites you allow your employees to access. You can even go as far as to customize which employee can go to which website. For example, a marketing coordinator might need access to Facebook while an accountant doesn’t. Using web filtering, will cut down on time wasted by employees and hopefully increase productivity within your company.
 File this one away under “obscure and terrifying.�
 “Fool me once, shame on you. Fool me twice, shame on me,” as the saying goes. Unfortunately, Google has now been fooled by the same trick twice.
 If you own a smartphone made by Chinese manufacturer OnePlus, you can thank security researcher Chris Moore for making a discovery that the manufacturer wasn’t going to tell you about.




